Brian Donohue

About

“We are what we pretend to be, so we must be careful about what we pretend to be.” ― Kurt Vonnegut

Apache Server-Status Publicly Viewable on Top Sites

A vast number of websites ranging from obscure to quite popular have left an Apache Web server functionality called server-status enabled and publicly accessible. The care-less implementation of this module, Securi CTO Daniel Cid warns in a write-up on Securiblog, could give potential attackers valuable information to help launch targeted attacks.
Trouble for Borderlands 2 Players

Some XBOX Live users have violated the online gaming platform’s code of conduct by using a malicious application that allowed them to permanently kill off the characters of other players in the popular ‘Borderlands 2’ video game.

Point-of-Sale Terminals Compromised at 63 Barnes & Noble Locations

UPDATE – America’s largest book retailer, Barnes & Noble, announced this morning it has detected evidence of tampering in 63 PIN-pad devices used in as many stores by criminals trying to steal payment card information. Barnes & Noble claims to have disconnected all the affected devices from service on Sept. 14. The retailer did not disclose how many customers may have been affected by the tampered devices.


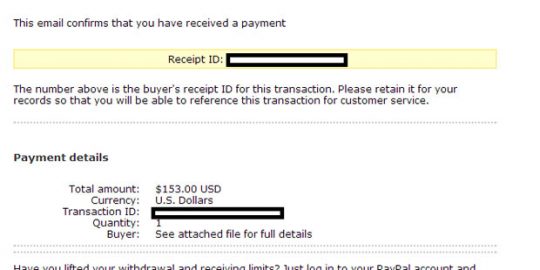
Cybercriminals are mimicking the online payment processor PayPal in a malicious spam campaign that attempts to dupe customers into downloading malware from links in seemingly authentic emails, according to a Webroot report written by Dancho Danchev.

Please leave your credit card number, its expiration date and security code, along with your full name and billing address in the comments section of this blog post. You’re obviously not going to do this. You know better, I know better, but there are those who don’t. So many, in fact, that scammers are not only comfortable with and willing to invest in scams no more or less complicated, but they are also confident that the scams will succeed.

A zero-day vulnerability in Novell ZENworks Asset Management Software 7.5 gives access to any files with system privileges and could also allow an attacker to grab configuration parameters, including the backend credentials in clear text, according to Rapid7 exploit developer Juan Vazquez who discovered the vulnerability and wrote an exploit module for Metasploit