Chris Brook

About

"Distrust and caution are the parents of security" - Benjamin Franklin

Report: Fraudulent Calls Up 29 Percent in 2012

On average, there were almost five fraudulent phone calls every minute earlier this year according to a report released today from security firm Pindrop Security. The Atlanta-based company found phone fraud was up 29 percent January to June this year from the last half of 2011 after it analyzed 1.3 million different instances as part of its 2012 State of Phone Fraud Report.
Dropbox Blames Breach for Recent Spam Targeting Customers

Over the last few weeks an attacker used a collection of illicitly obtained usernames and passwords to infiltrate a number of Dropbox accounts, including one belonging to a Dropbox employee. The usernames and passwords were stolen from other, third-party websites, Dropbox officials said, finally confirming the breach, which had been rumored for several weeks.

Firm Sees More DDoS Attacks Aimed at Telecom Systems

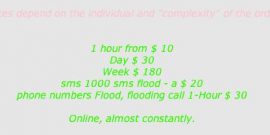
Attackers are now using DDoS services that offer attacks on telecommunication systems as part of larger attack schemes. These attacks, known as TDoS attacks, can be a relatively cheap option for cybercriminals looking into diversifying their attack vectors.


Two men have been arrested in South Korea for allegedly leaking the information of almost nine million of the nation’s mobile phone users, including details of the users’ monthly plans, according to a report issued by the Korea National Police Agency’s (KNPA) Cyber Terror Response Center (CTRC) over the weekend.

German industrial control system manufacturer Siemens announced Monday that it had patched holes in some of its products that appear to resemble holes used by the famous Stuxnet worm in 2010. If left unpatched, vulnerabilities in the company’s Simatic STEP 7 and Simatic PCS 7 software could have allowed the loading of malicious Microsoft Dynamic-link Library files. This in turn could lead to an attack against systems that use STEP 7, a la Stuxnet.

German industrial control system manufacturer Siemens announced Monday that it had patched holes in some of its products that appear to resemble holes used by the popular Stuxnet worm in 2010.If left unpatched, vulnerabilities in the company’s Simatic STEP 7 and Simatic PCS 7 software could have allowed the loading of malicious Microsoft Dynamic-link Library files. This in turn could lead to an attack against systems that use STEP 7.