Chris Brook

About

"Distrust and caution are the parents of security" - Benjamin Franklin

Did A Decade-Long Hack Trigger Nortel’s Demise?

A day after it was announced that Canadian telecommunications firm Nortel had been hacked for nearly 10 years, a prominent expert on sophisticated cyber attacks says the lengthy breach may have contributed to the company’s eventual collapse.

Slideshow: Scenes from SAS 2012

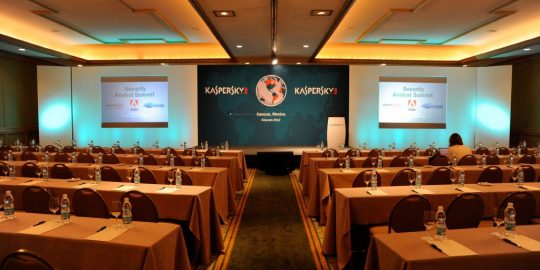
VIEW SLIDESHOW Scenes from SAS 2012At Kaspersky Lab’s Security Analyst Summit last week, over 100 researchers and law enforcement officials converged in Cancun, Mexico over the course of five days to network and discuss a veritable cornucopia of security topics. Topics such as privacy, SCADA and PLC security, tracking cybercriminals and the evolution of malware were discussed in depth.


Microsoft released nine security updates Tuesday, four critical; five important, fixing 21 different holes in various applications with its February patch release. The four critical fixes deal with vulnerabilities in the company’s Windows, Internet Explorer, .NET Framework and Silverlight programs that could allow remote code execution if left unpatched.

Microsoft will issue nine security updates, four critical, for Patch Tuesday next week, fixing 21 different vulnerabilities in Windows, Internet Explorer, .NET, Silverlight and Office.Seven of the nine may lead to remote code execution, while the other two may lead to elevation of privilege, according to Microsoft’s advance notification bulletin yesterday.

Greg Hoglund

In his presentation on Friday, “Lateral Movement and Other APT Interaction Patterns within the Enterprise,” HBGary CEO Greg Hoglund reviewed a multitude of modern day Advanced Persistent Threats (APTs) while breaking down the four stages of an attack.

Terry McCorkle

Terry McCorkle, a Seattle-based researcher presented the results of an independent study on Supervisory Control and Data Acquisition Systems (SCADA) and Industrial Control Systems (ICS) where he and his research partner Billy Rios attempted to find 100 bugs in 100 days. They wound up finding 1000+ bugs in 8-9 months, 95 that were easily exploitable. McCorkle went on to call many of them “blatantly obvious” and “straight outta of the ‘90s.”

Denis Nazarov

Gathering his statistics from the Kaspersky Security Network, Denis Nazarov, head of Kaspersky Lab’s Anti-Malware Research US, compared infection rates on x86 and x64 versions of Windows while describing Kernel Patch Protection technology.

In a presentation on the second day, “Humans Are the Weakest Link,” Valery Boronin, Director DLP Research, R&D at Kaspersky Lab and Vera Trubacheva, a System Analyst at Kaspersky Lab, put DLP 1.0 (or at least a small stuffed animal) on trial, so to speak. Underscoring that when it comes down to it, end-users are responsible for security, the two discussed why human awareness is of the utmost importance when it comes to understanding potential security threats.

Investigators from Interpol, the Dutch High Tech Crime Unit (NHTCU), Germany’s Bundeskriminalamt (BKA), and the General Directorate for the Romanian Intelligence and Internal Protection (GDIIP) participated in a panel moderated by Threatpost editor Paul Roberts on the first day of the conference. The officials stressed that stagnant law, a lack of internal cooperation and advocates staunchly in favor of privacy frequently impede justice.