Dennis Fisher

About

Dennis Fisher is a journalist with more than 13 years of experience covering information security.

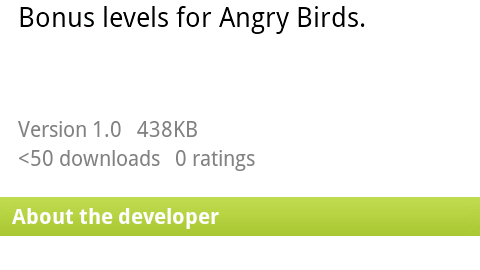
Image of the Day: Fake Angry Birds Android App

Security researcher Jon Oberheide wrote a fake extension to the popular Angry Birds mobile game and put it in the Android Market as a demonstration of how an attacker could exploit a vulnerability he’d found in Android. The phony app didn’t do anything malicious, but it had permissions on Android handsets that enabled it to send toll SMS messages, steal contacts and take other actions, without the user’s knowledge.
Dissecting the ZeroAccess Rootkit

The ZeroAccess rootkit isn’t the most well-known or closely watched piece of malware in recent history, but, as an extremely detailed new analysis of the program shows, it is a perfect example of the kind of sophisticated malware that attack crews are using to maintain persistent, silent access to compromised machines.

Hardcoded Password, Other Critical Bugs Found in Cisco UVC Software

There is a series of vulnerabilities in Cisco’s Unified Videoconferencing product, including a hardcoded password for several powerful accounts that can’t be changed or deleted. That bug and others disclosed Wednesday can be used to gain complete control of the device and possibly compromise other parts of the internal network.


In recent versions of Windows, specifically Vista and Windows 7, Microsoft has introduced a number of new security features designed to prevent malicious code from running. But attackers are continually finding new ways around those protections, and the latest example is a rootkit that can bypass the Windows driver-signing protection.

As part of its continuing focus on collecting information on data breaches and thefts, Verizon Business has released VERIS Community application, a new application that enables security professionals to enter anonymous information about an incident and receive a detailed report in return.

WASHINGTON–Despite its reputation for secrecy and technical expertise, the National Security Agency doesn’t have a set of secret coding practices or testing methods that magically make their applications and systems bulletproof. In fact, one of the agency’s top technical experts said that virtually all of the methods the NSA uses for development and information assurance are publicly known.