Dennis Fisher

About

Dennis Fisher is a journalist with more than 13 years of experience covering information security.

Certificate Transparency Moves Forward With First Independent Log

The Certificate Transparency scheme proposed by Google engineers has taken a couple of significant steps forward recently, with the approval of the first independent certificate log and the passing of a deadline for all extended validation certificates to be CT-compliant or lose the green indicator in Google Chrome. On Jan. 1, a CT log operated by […]
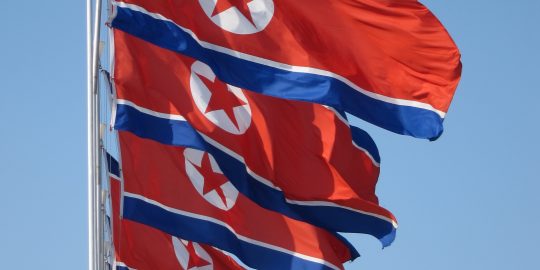
Inside North Korea’s Naenara Browser

Up until a few weeks ago, the number of people outside of North Korea who gave much thought to the Internet infrastructure in that country was vanishingly small. But the speculation about the Sony hack has fixed that, and now a security researcher has taken a hard look at the national browser used in North […]

Root Command Execution Flaw Haunts ASUS Routers

There is a serious security vulnerability in the firmware of many ASUS routers that allows unauthenticated command execution. The bug may be present in all current versions of the router firmware, and there is an exploit published for it, as well. Security researchers Joshua Drake posted an advisory on the vulnerability on Thursday, detailing the bug […]


The OpenSSL Project has released several new versions of the software that fix eight security vulnerabilities, including several certificate issues and a couple of denial-of-service flaws. The patches included in OpenSSL 1.0.0p, 1.0.1k and 0.98zd are not for critical or high-risk vulnerabilities, but they do fix some interesting vulnerabilities. Two of the bugs are rated moderate and the other […]

Security researchers are tracking a new version of the Emomet malware that is targeting users’ banking credentials and also has the ability to steal email usernames and passwords, which are then used to send spam from compromised accounts. The new variant of Emomet has mostly been seen targeting users in Germany, but researchers at Microsoft […]

HP’s Zero Day Initiative has decided to adjust its guidelines and criteria or buying some vulnerabilities in the future, eliminating some large classes of bugs from its menu. The group, which has been among the more visible and prominent of the vulnerability purchasing programs since its inception several years ago, has decided that it will […]

The attackers behind the SoakSoak malware campaign are continuing to modify their tactics and have infected a new group of Web sites. The Javascript code that the attackers target with the malware has also changed. Last week, Google took the step of blacklisting thousands of sites that had been infected by SoakSoak. The malware is targeting WordPress […]