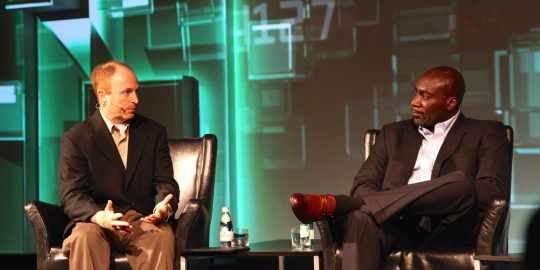
Financial Services Companies Facing Varied Threat Landscape
Financial services organizations must contend with not only advanced hackers, but also common malware attacks, panelists said at the Kaspersky Lab Cyber Security Summit.

About
Dennis Fisher is a journalist with more than 13 years of experience covering information security.
Financial services organizations must contend with not only advanced hackers, but also common malware attacks, panelists said at the Kaspersky Lab Cyber Security Summit.
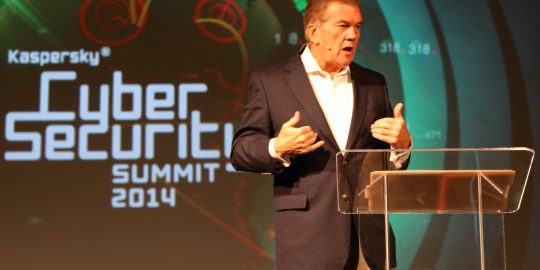
Former DHS secretary Tom Ridge said at the Kaspersky Lab Cybersecurity Summit that U.S. critical infrastructure will be a target as long as the public and private sector balk on sharing attack and threat data.

Vendors are continuing to check their products for potential effects from the OpenSSL heartbleed vulnerability, and both Cisco and BlackBerry have found that a variety of their products contain a vulnerable version of the software. BlackBerry on Thursday said that several of its software products are vulnerable to the OpenSSL bug, but that its phones […]

Google is adding a new security feature to Android designed to scan installed apps on a device and ensure that they’re not acting maliciously or taking unwanted actions. The system is built on Google’s existing app-verification model, which warns users if there’s a potential problem with an app they’re installing. The addition to Android’s security […]
There’s nothing the Internet loves more than a fat, juicy story that it can sink its sharpened, yellowing canines into. And for the security community, the OpenSSL heartbleed vulnerability has been the equivalent of a 72-ounce steak. But an Internet-breaking vulnerability like this one is no good unless we can learn something from it (or […]
The list of products and sites affected by the OpenSSL heartbleed vulnerability continues to grow, and as security teams implement the patch and dig into the thornier work of revoking certificates, a new problem is emerging: It’s difficult to know whether an attacker has exploited the vulnerability on a given system.
The BEAST attack on some TLS implementations made major news when it was disclosed, showing that attackers could intercept and decrypt SSL-protected sessions in real time, breaking a significant portion of the confidentiality model of the protocol. Vendors rushed to patch and implement mitigations. That was in 2011. Nearly three years later, Siemens is pushing […]

Google has patched a long list of serious security vulnerabilities in Chrome, including at least 19 highly rated flaws. The company patched a total of 31 vulnerabilities in Chrome 34 and paid out more than $28,000 in rewards to researchers who reported bugs to Google. Among the security fixes in Chrome 34 are patches for […]

Site operators and software vendors are scrambling to fix the OpenSSL heartbleed bug revealed Monday, a vulnerability that enables an attacker to extract 64 KB of memory per request from a server
The maintainers of the OpenSSL library, one of the more widely deployed cryptographic libraries on the Web, have fixed a serious vulnerability that could have resulted in the revelation of 64 KB of memory to any client or server that was connected.
Infosec Insider content is written by a trusted community of Threatpost cybersecurity subject matter experts. Each contribution has a goal of bringing a unique voice to important cybersecurity topics. Content strives to be of the highest quality, objective and non-commercial.
Sponsored Content is paid for by an advertiser. Sponsored content is written and edited by members of our sponsor community. This content creates an opportunity for a sponsor to provide insight and commentary from their point-of-view directly to the Threatpost audience. The Threatpost editorial team does not participate in the writing or editing of Sponsored Content.


