Dennis Fisher

About

Dennis Fisher is a journalist with more than 13 years of experience covering information security.

facebook .onion

Tor Users Hit With Firefox Exploit, But No Large Compromise of Network Seen

The vulnerability in Firefox that was being used to exploit some users of Tor in recent days was fixed in a previous Firefox release and the exploit in circulation only works against people running Firefox 17. Over the weekend, word spread that the exploit was in the wild and that the Tor network itself had been compromised, however Tor officials said that was not the case and it was one specific hosting provider who hosts some Tor Hidden Services servers that had been targeted.
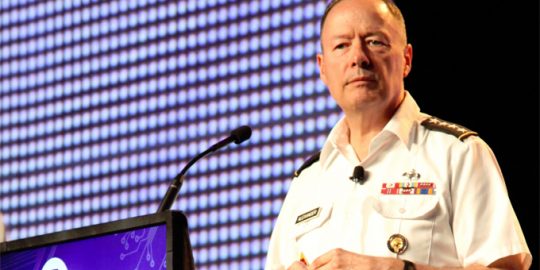
VIDEO: Gen. Keith Alexander at Black Hat

When Gen. Keith Alexander, the director of the National Security Agency and chief of U.S. Cyber Command, agreed to deliver the opening keynote at Black Hat USA 2013, he had no idea that by the time he took the stage many of the NSA’s most secret information-collection programs would be public knowledge, thanks to Edward Snowden.

Jason Geffner on Tortilla

Dennis Fisher talks with Jason Geffner of CrowdStrike about the new tool he released at Black Hat called Tortilla and his research on malware that uses domain-generating algorithms.


Security researchers have been warning about the weaknesses and issues with JavaScript and iframes for years now, but the problem goes far deeper than even many of them thought. A researcher in the U.K. has developed a new technique that uses a combination of JavaScript-based timing attacks and other tactics to read any information he wants from a targeted user’s browser and sites the victim is logged into. The attack works on all of the major browsers and researchers say there’s no simple fix to prevent it.

The pervasive bulk surveillance performed by the NSA and other government agencies that’s been revealed in recent weeks relies on court orders, as do other kinds of legal access operations, such as wiretapping or lawful intercepts. Those orders are shrouded in secrecy and the organizations that receive them often comply immediately without asking any questions, a response that can sometimes be a mistake.

When a new piece of malware surfaces, it’s typically analyzed eight ways from Sunday by a long list of antimalware and other security companies, government agencies, CERTs and other organizations who try to break it down and classify its capabilities. There’s a lot of duplicated effort there, and a group of researchers is building a new tool called CrowdSource that is designed to take advantage of the existing analysis capabilities in the community and perform automated malware analysis to provide rich reports on each new sample.

Microsoft is expanding its MAPP program that shares attack and protection information with other security vendors and will now be sharing some data with incident responders, as well. The new system will enable organizations such as CERTs and internal IR teams to exchange information on specific attacks and general threats.

It’s said that each man’s death diminishes us all in some way. But some passings take a bigger piece than others. The death of Barnaby Jack is one of those, having left a major hole in the security community and let a lot of air out of the room.