Twitter Bug Allowed Apps to Access Direct Messages Without Permission
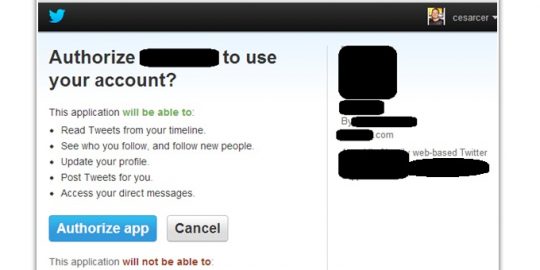
Social networking sites such as Twitter and Facebook have become not just communication hubs, but also authentication mechanisms for third-party sites. Many sites and Web applications allow users to sign in with their Facebook or Twitter credentials rather than registering, which is a nice convenience. That is, until, it turns into a security liability. Security researcher Cesar Cerrudo recently discovered a bug in Twitter’s code that enabled third-party apps to access users’ private direct messages under some circumstances, even when users had not explicitly granted those apps that level of access.