
Microsoft: Attackers Tried to Login to SolarWinds Serv-U Via Log4j Bug
UPDATE: SolarWinds has fixed a Serv-U bug discovered when attackers used the Log4j flaw to try to log in to the file-sharing software.
UPDATE: SolarWinds has fixed a Serv-U bug discovered when attackers used the Log4j flaw to try to log in to the file-sharing software.
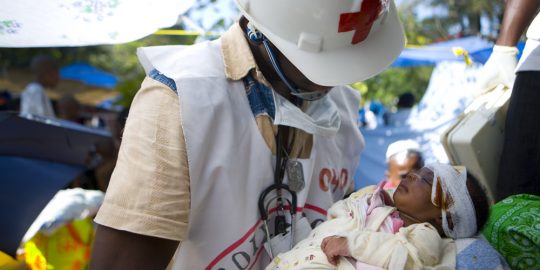
A cyberattack forced the Red Cross to shut down IT systems running the Restoring Family Links system, which reunites families fractured by war, disaster or migration. UPDATE: The ICRC says it’s open to confidentially communicating with the attacker.

Praise be & pass the recipe for the software soup: There’s too much scrambling to untangle vulnerabilities and dependencies, say a security experts roundtable.

It’s a double-extortion play that uses the command-line password ‘KissMe’ to hide its nasty acts and adorns its ransom note with cutesy ASCII bunny art.

As Moscow moves troops and threatens military action, about 70 Ukrainian government sites were hit. “Be afraid” was scrawled on the Foreign Ministry site.

Since their release on Patch Tuesday, the updates have been breaking Windows, causing spontaneous boot loops on Windows domain controller servers, breaking Hyper-V and making ReFS volume systems unavailable.

US Cyber Command linked the group to Iranian intelligence and detailed its multi-pronged, increasingly sophisticated suite of malware tools.

Most Windows versions are at risk of remote, unprivileged attackers abusing RDP from the inside to hijack smart cards and get unauthorized file system access.

The flaw could allow attackers to bypass Privacy preferences, giving apps with no right to access files, microphones or cameras the ability to record you or grab screenshots.

The FBI warned that attackers are impersonating Health & Human Services and/or Amazon to mail BadUSB-poisoned USB devices to targets in transportation, insurance & defense.
Infosec Insider content is written by a trusted community of Threatpost cybersecurity subject matter experts. Each contribution has a goal of bringing a unique voice to important cybersecurity topics. Content strives to be of the highest quality, objective and non-commercial.
Sponsored Content is paid for by an advertiser. Sponsored content is written and edited by members of our sponsor community. This content creates an opportunity for a sponsor to provide insight and commentary from their point-of-view directly to the Threatpost audience. The Threatpost editorial team does not participate in the writing or editing of Sponsored Content.


