Michael Mimoso

Pwn2Own IE Vulnerabilities Missing from Microsoft Patch Tuesday Updates

UPDATE – In an unexpected turn, Microsoft’s monthly Patch Tuesday security updates released today did not include patches for Internet Explorer vulnerabilities used during the Pwn2Own contest one month ago.The popular hacker contest attracted researchers from all over who were targeting all the major browsers, as well as third-party software such as Flash and Java.
Appropriately enough for the start of the baseball season, Microsoft is going to go 4-for-4 and release another set of critical Internet Explorer patches on Tuesday, the fourth consecutive month in which serious vulnerabilities in the browser are being addressed in Microsoft’s Patch Tuesday monthly security updates.

Security-related policy or legislation is enacted and then enforced to protect corporate, government or military interests. Civil organizations are often left flailing in the wind, fending for themselves with fewer IT resources and experience than a Middle America mom-and-pop operation. Yet these non-governmental—and not-for-profit—organizations have tasked themselves with helping those targeted by lethal adversaries who aren’t just after corporate secrets, but are out to deny people their freedom or, in some cases, their lives.

Tibetan activists in China as well as those living in exile around the world are being targeted by dangerous malware that not only steals data from infected computers, but also has graduated to reporting location data from mobile devices for surveillance purposes.

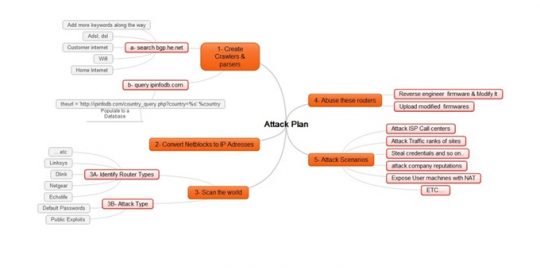
It’s the ultimate what-if scenario: What if an attacker could own all the customer premises equipment (CPE) doled out by ISPs such as routers and modems? Would it be trivial with available scanning equipment and other tools to find vulnerable gear, and then modify and re-upload the firmware to be able do anything such as control Web traffic, launch DDoS attacks, or even disconnect large blocks of machines from the Internet?