Michael Mimoso

Active Defense Drives Attack Costs Up

While every corporate general counsel, CIO and anyone with a CISSP will tell you that hacking back against adversaries is illegal and generally a bad thing to do, there are alternatives that companies can use to gain insight into who is behind attacks, collect forensic evidence and generally confound hackers, perhaps to the point where they veer away from your network.

Three Charged with Creating, Distributing Gozi Banking Malware

Charges will be brought today in the U.S. District Court for the Southern District of New York against three men allegedly involved with creating and distributing the Gozi banking Trojan. Gozi infected more than a million computers worldwide, including a handful at NASA, leading to tens of millions of dollars in lost banking funds and damages to computer systems and networks.

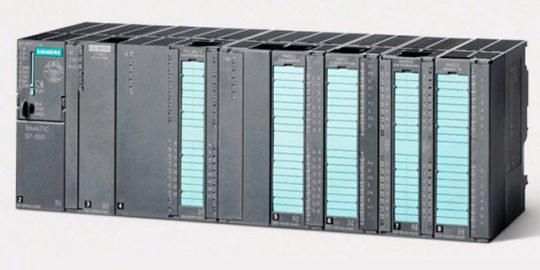
Password Cracker Targets Siemens S7 PLCs

Siemens S7 programmable logic controllers, the same PLC family exploited by the Stuxnet malware, are in the crosshairs of a password-cracking tool that is capable of stealing credentials from industrial control systems.


Rarely a day goes by without mention of a targeted attack against some government-related website, massive disruptions in online banking services, or critical vulnerabilities in specialized software running our power plants and water supplies. And all the while, IT and security organizations have thought little about fighting back. Their options were limited to better patching, more security hardware and new firewall rules. That dynamic is changing because the buzzwords active defense and hacking back are creeping into conversations between vendors and customers, IT managers and executives, executives and legal teams. 

With Skype expanding its reach with services designed for small businesses, and other messaging platforms such as Microsoft Windows Messenger shutting down, Skype is becoming an attractive target for malware writers.Reports surfaced last week of the Shylock financial malware spreading on Skype and yesterday, researchers reported the discovery of more malware propagating on Skype.  

How many inconspicuous botnets are alive and siphoning banking credentials and real money from online accounts that get little to no attention? They feast on unwitting consumers using an array of available banking Trojans to steal legitimate log-in information and sell it to the highest bidder, often with great success because they got lost in the sea of similar campaigns. Researchers at Dutch security company Fox-IT recently took apart an average botnet running amok in the Netherlands called Pobelka, a Russian word that means whitewash (perhaps a euphemism for money laundering). The analysis paints a picture of the simplicity with which even a small criminal organization can spread malware for profit, virtually unscathed.

Just when you thought phishers had exhausted all avenues of innovation, a new tactic has emerged in attacks against financial institutions bringing the level of targeting and geo-filtering to precise new levels. Dubbed bouncer list phishing by RSA Security, these attack kits are built off stolen email lists that are filtered for particular targets, such as a regional bank.