Scope of ThinkPwn UEFI Zero Day Expands
The scope of the ThinkPwn UEFI vulnerability disclosed last week has grown past Lenovo and HP laptop firmware to motherboards sold by Gigabyte.

The scope of the ThinkPwn UEFI vulnerability disclosed last week has grown past Lenovo and HP laptop firmware to motherboards sold by Gigabyte.

A team of academics and researchers has developed a technique called selfrando that it says can defend against attacks that unmask users of the Tor Network.
Jkanime, a popular site that streams anime videos, has been infected with malware that redirects to the Neutrino Exploit Kit and CryptXXX ransomware infections.

Researchers at Rapid7 found a vulnerability in the Swagger Code Generator that could execute arbitrary code embedded in a Swagger document.

WordPress updated to version 4.5.3, a security release for all versions.
Libarchive was patched against three memory-related vulnerabilities, putting pressure on admins to ensure third-party software that also uses the library is patched.

Researchers who study exploit kits are reporting that two major kits, Angler and Nuclear, may no longer be available.

Advantech has published a new version of its WebAccess product to address vulnerabilities that put installations at risk to remote code execution attacks.
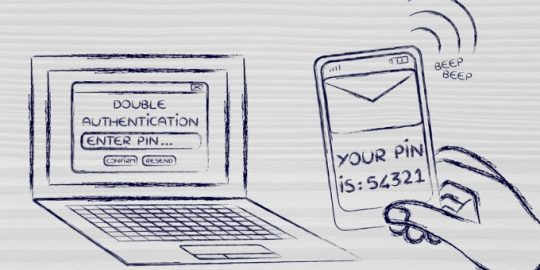
Google has simplified its 2-step verification feature with a basic prompt users can take advantage of as a second form of authentication.

The Department of Defense last week released the results of the first Hack the Pentagon bounty program and 18-year-old David Dworken was among those who participated.
Infosec Insider content is written by a trusted community of Threatpost cybersecurity subject matter experts. Each contribution has a goal of bringing a unique voice to important cybersecurity topics. Content strives to be of the highest quality, objective and non-commercial.
Sponsored Content is paid for by an advertiser. Sponsored content is written and edited by members of our sponsor community. This content creates an opportunity for a sponsor to provide insight and commentary from their point-of-view directly to the Threatpost audience. The Threatpost editorial team does not participate in the writing or editing of Sponsored Content.


