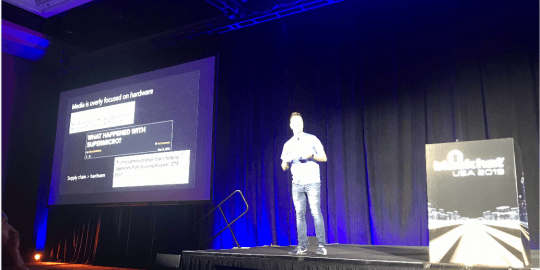
Black Hat 2019: Addressing Supply-Chain Risk Starts with People, Microsoft Says
Hardware, software, services and people make up supply-chain risk — but the latter should be the guiding focus.
About
Tara Seals has nearly 25 years of experience as a journalist, analyst and editor in the communications and technology space. Prior to Threatpost, Tara was the North American news lead for Infosecurity Magazine, and spent 13 years working for Informa (formerly Virgo Publishing), as executive editor and editor-in-chief at publications focused on both the service provider and the enterprise arenas. A Texas native, she holds a B.A. from Columbia University, lives in Western Massachusetts with her family and is on a never-ending quest for good Mexican food in the Northeast.
Hardware, software, services and people make up supply-chain risk — but the latter should be the guiding focus.

The vulnerability is a decade old with a public exploit, yet remained unpatched in one of the phone giant’s most popular models.
A pair of reports released at Black Hat mark the huge shift away from targeting consumers.
An ongoing campaign is hosting its phishing landing pages on enterprise-class public cloud storage services — a nascent trend meant to throw defenders off.
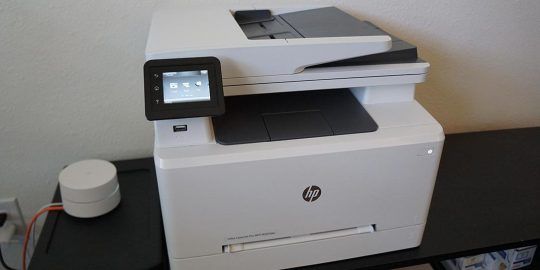
A raft of bugs in six popular models can allow a hacker to wreak havoc on a corporate network.

Academic researchers carry out attacks on high-end commercial devices as well as narrowband IoT sensors.

Dino Dai Zovi, mobile security lead at Square, discusses ongoing transformation in security’s role in the workplace during the keynote.

The adversaries have retooled with EternalBlue and credential theft to add a new “access mining” revenue stream.

A new type of malicious plugin has been spotted in the wild with the capability of targeting individual blog posts.

The sites are targeting job-seekers, movie aficionados and shoppers in hopes of harvesting their personal information.
Infosec Insider content is written by a trusted community of Threatpost cybersecurity subject matter experts. Each contribution has a goal of bringing a unique voice to important cybersecurity topics. Content strives to be of the highest quality, objective and non-commercial.
Sponsored Content is paid for by an advertiser. Sponsored content is written and edited by members of our sponsor community. This content creates an opportunity for a sponsor to provide insight and commentary from their point-of-view directly to the Threatpost audience. The Threatpost editorial team does not participate in the writing or editing of Sponsored Content.


