libssh Authentication Bypass Makes it Trivial to Pwn Rafts of Servers
The flaw affects thousands of servers; but GitHub, a major libssh user, is unaffected.
The flaw affects thousands of servers; but GitHub, a major libssh user, is unaffected.

Gym customer data, including contact information, birth dates and height/weight data, opens the door to convincing follow-on social-engineering attacks.
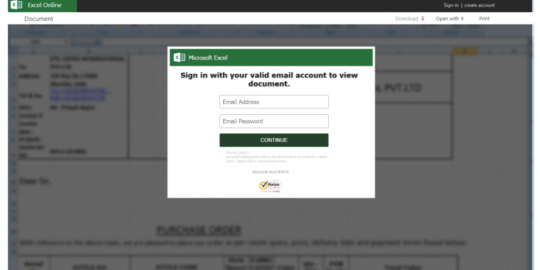
A brand-new approach to harvesting credentials hinges on users’ lack of cloud savvy.

This year’s Virus Bulletin conference featured top-tier research from some of the world’s best threat intelligence experts.

Cloud computing is creating new challenges among security professionals as attackers embrace the “as-a-service model”, giving unsophisticated cybercriminals a leg up in carrying out attacks.

Google was caught not disclosing a potential data breach — leaving questions as to whether a lack of transparency is the new normal.

A converged architecture that brings independent software vendors, cloud vendors and IoT vendors together is reshaping the security landscape.

Supply-chain attacks are on the rise, but machine learning provides the edge that the security industry needs to keep up.

Attractive to both white-hats and cybercriminals, AI’s role in security has yet to find an equilibrium between the two sides.

Businesses are increasingly adopting artificial intelligence, but all too often these platforms don’t feature security-by-design.
Infosec Insider content is written by a trusted community of Threatpost cybersecurity subject matter experts. Each contribution has a goal of bringing a unique voice to important cybersecurity topics. Content strives to be of the highest quality, objective and non-commercial.
Sponsored Content is paid for by an advertiser. Sponsored content is written and edited by members of our sponsor community. This content creates an opportunity for a sponsor to provide insight and commentary from their point-of-view directly to the Threatpost audience. The Threatpost editorial team does not participate in the writing or editing of Sponsored Content.


