Weak Homegrown Crypto Dooms Open Smart Grid Protocol
Researchers in Europe have published research examining weak, homegrown cryptography used in the Open Smart Grid Protocol.
Researchers in Europe have published research examining weak, homegrown cryptography used in the Open Smart Grid Protocol.
The SANS Institute reports a new strain of CTB-Locker ransomware moving this week via spam messages.

A Congressional hearing on encryption and “frontdoors” produced a generous amount of the usual “crazy” from lawmakers and law enforcement.
Heartbleed made the world notice what kind of shape OpenSSL development was in from a financial and resources standpoint. In the year since, the project has been funded enough to hire full-time engineers and a crucial refactoring of the codebase has the project in the right direction.
Mozilla is removing a Turkish root CA from the Firefox trust store, not because of a compromise or a mistakenly issued certificate, but because the certificate authority hasn’t lived up to the audit requirements Mozilla has for trusted CAs. Like other browser vendors, Mozilla has a lengthy policy that sets out the requirements for CAs to […]
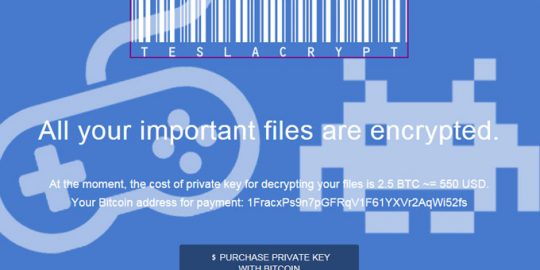
Cisco published an analysis of TeslaCrypt and a decryptor tool that recovers files lost to the ransomware.

A few weeks after the developers of the AFNetworking library that’s popular among iOS and OS X app developers patched a serious bug in the library that enabled man-in-the-middle attacks, another, similar flaw has surfaced. The new vulnerability is related to how the AFNetworking library handles domain name validation for certificates. As it turns out, the library […]

SAN FRANCISCO–The more things change, the more they stay the same. Thirty years ago, Adi Shamir, one of the inventors of the RSA algorithm, was asked to do a keynote speech at a conference and spoke about his laws of computer security. They were a set of principles that he developed over the years relating […]
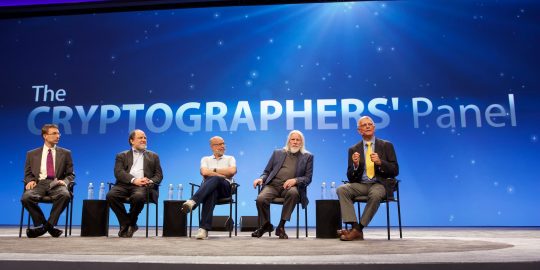
SAN FRANCISCO–Encryption is the hot new topic in security at the moment, as it has been any number of times in the last few decades. And, as in the past, the notions of key escrow, mandated legal access to encrypted systems and other ideas for helping governments defeat cryptosystems have followed right along with the latest crypto […]

Google engineers have spent the last several years moving many of the company’s online services to encrypted links. Gmail is HTTPS by default, and Google search is done over SSL for much of the world. Now the company is working to move its ad-serving and ad-buying platforms to HTTPS, as well. Google’s ad networks are pervasive […]
Infosec Insider content is written by a trusted community of Threatpost cybersecurity subject matter experts. Each contribution has a goal of bringing a unique voice to important cybersecurity topics. Content strives to be of the highest quality, objective and non-commercial.
Sponsored Content is paid for by an advertiser. Sponsored content is written and edited by members of our sponsor community. This content creates an opportunity for a sponsor to provide insight and commentary from their point-of-view directly to the Threatpost audience. The Threatpost editorial team does not participate in the writing or editing of Sponsored Content.


