Cryptography


Google Strengthening Keys on SSL Certificates to 2048 Bits

As attacks against cryptographic systems and the SSL infrastructure have advanced in recent years, experts have begun to fret about the future utility of the system. Companies that rely on the security of the SSL technology are beginning to take steps to address the issue, with the latest being Google, which is planning to change […]


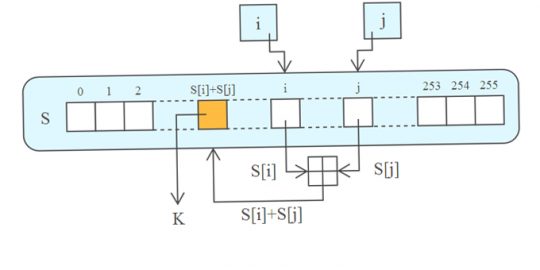
It’s been more than 25 years since Ron Rivest invented his RC4 stream cipher, and after all that time it’s still being used widely, which is something of an achievement in the crypto world. However, for more than 15 years researchers have known about a weakness in RC4 that could enable an attacker to decrypt the keystream. Now, a cryptographer has published an attack that exploits that vulnerability and causes serious problems with TLS implementations.

SAN FRANCISCO–In the current climate of continuous attacks and intrusions by APT crews, government-sponsored groups and others organizations, cryptography is becoming less and less important and defenders need to start thinking about new ways to protect data on systems that they assume are compromised, one of the fathers of public-key cryptography said Tuesday. Adi Shamir, who helped design the original RSA algorithm, said that security experts should be preparing for a “post-cryptography” world.

Passwords are the keys to our online identities, and as a result, they’re also near the top of the target list for attackers. There have been countless breaches in the last few years in which unencrypted passwords have been stolen from a database and leaked online, and security experts often shake their heads at the lack of use of encryption or even hashing for passwords. Now, a group of cryptographers is sponsoring a competition to come up with a new password hash algorithm to help improve the state of the art.

A group of large certificate authorities, including some that have been the victims of recent compromises of their CA systems, have formed an alliance designed to develop strategies for strengthening the CA infrastructure through education and industry initiatives. Comodo, DigiCert, Entrust, Symantec and Go Daddy and other companies announced the alliance on Thursday.