Government


DoD Inspector General Calls Out Army CIO For Poor Mobile Device Security

The CIO of the U.S. Army failed to put in place a comprehensive security program capable of protecting data stored on commercial mobile devices such as iPhones and Androids, leaving sensitive information in key Army installations exposed. The Inspector General of the Department of Defense took the Army CIO to task in a new report, saying that the CIO “did not implement an effective cybersecurity program for [commercial mobile devices]”.

Spear Phishing Cause of South Korean Cyber Attack

It appears that a spear phishing campaign was the genesis for the wiper malware infections that ultimately knocked several prominent South Korean banks and broadcasters offline last week, according to a malware analysis performed by researchers from the Finnish cybersecurity firm F-Secure.

Experts Tell Congress Serious Deterrence Needed to Impede Foreign Cyber Attacks

The House Foreign Affairs Subcommittee on Europe, Eurasia, and Emerging Threats typically is more concerned with economics and political issues than cyber attacks, but the members spent this morning in a hearing trying to come up with an answer to a fairly straightforward, but thorny question: What consequences are serious and meaningful enough that they will deter U.S. enemies from infiltrating the country’s networks?


Researchers have uncovered a long-term cyber-espionage campaign that used a combination of legitimate software packages and commodity malware tools to target a variety of heavy industry, government intelligence agencies and political activists. Known as the TeamSpy crew because of its affinity for using the legitimate TeamViewer application as part of its toolset, the attackers may have been active for as long as 10 years, researchers say.

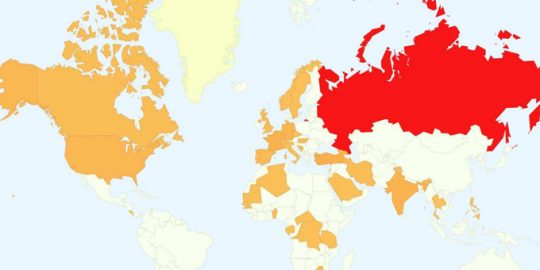
Politicians, security researchers and others involved in the fight against cybercrime often compare the situation to efforts to combat traditional organized crime. Some of the tricks and tactics are comparable, and so are the motives, but there’s one major difference between the two groups: Cybercriminals have virtually no fear of being caught. The chances of a cybercriminal being caught, prosecuted and actually serving time in prison are incredibly small, especially in relation to the volume of cybercrime activity occurring today.

VANCOUVER–When Peiter Zatko, the security researcher and pioneering hacker known as Mudge, joined the federal government several years ago to help run a DARPA research program, some in the security industry wondered what effect someone with his background could have in an organization as famously change-resistant and slow as the Department of Defense. As it turns out, the Cyber Fast Track program he started has been a huge success and though the CFT is ending in less than a month, the program may well serve as a model for other agile research programs inside the U.S. government.