DHS Appeals to Users Still Infected with DNSChanger
The Department of Homeland Security is the latest agency to appeal to U.S. consumers to check their computers for signs of DNSChanger malware before they are knocked offline in a couple of months.
The Department of Homeland Security is the latest agency to appeal to U.S. consumers to check their computers for signs of DNSChanger malware before they are knocked offline in a couple of months.
The Dutch government has asked DigiNotar, the Dutch certificate authority that was broken into last summer, for €8.7 million ($11M USD) to recoup money it spent buying new certificates, according to several Dutch news reports. The Dutch interior ministry asked for €1 million in January, yet the number “has now risen to €8.7 million,” according to the company’s curator Rocco Mulder in an interview with Dutch news site nu.nl.
The U.S.’s Cyber Command is using special, classified briefings with private sector CEOs to scare them into greater vigilance about the threat of cyber attacks, according to an NPR report.
The Department of Homeland Security said it is investigating a string of cyber intrusions targeting companies that operate national gas pipelines in the U.S.
In an attempt to clear the cybersecurity air, the United States and the People’s Republic of China agreed Monday to work in tandem to prevent future cyber threats. Meeting at the Pentagon, Defense Secretary Leon Panetta and General Liang Guanglie, China’s Minister of National Defense, insisted the two nations should be seen as equals and according to Guanglie, “build a new state-to-state relationship that’s not a stereotype of two major powers predestined for conflict.”
The UK’s military’s head of cyber security warned that hackers have breached computer systems containing top secret data, The Guardian reported.
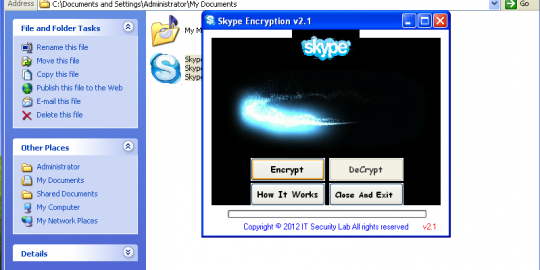
In Syria, the crackdown on political activists continues, with reports of pro-Syrians using malware that targets and spies on users attempting to use popular VOIP software Skype.
A report by the Federal Emergency Management Agency (FEMA) finds that state and local government officials in the U.S. are pessimistic about their ability to respond to a cyberattacks.
In a post on the F-Secure Labs blog, Chief Research Officer Mikko Hypponen says the firm received a hard drive image from a “contact” within Syria who believed that his computer had been compromised. An F-Secure analysis of the drive’s contents and Web history revealed evidence of a targeted attack that used a malicious Skype chat link to install a copy of Xtreme RAT, a remote access tool that’s commercially available online.
The Website of the United Kingdom’s Serious Online Crime Agency (SOCA) remains offline this morning following a distributed denial of service (DDoS) attack.
Infosec Insider content is written by a trusted community of Threatpost cybersecurity subject matter experts. Each contribution has a goal of bringing a unique voice to important cybersecurity topics. Content strives to be of the highest quality, objective and non-commercial.
Sponsored Content is paid for by an advertiser. Sponsored content is written and edited by members of our sponsor community. This content creates an opportunity for a sponsor to provide insight and commentary from their point-of-view directly to the Threatpost audience. The Threatpost editorial team does not participate in the writing or editing of Sponsored Content.


