Government


Slideshow: Scenes from SAS 2012

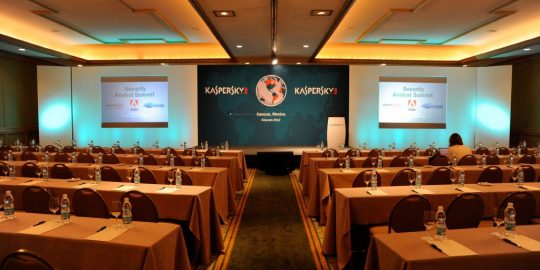
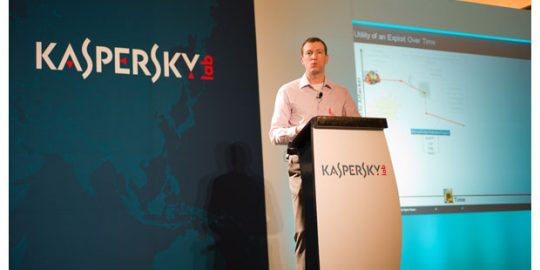
VIEW SLIDESHOW Scenes from SAS 2012At Kaspersky Lab’s Security Analyst Summit last week, over 100 researchers and law enforcement officials converged in Cancun, Mexico over the course of five days to network and discuss a veritable cornucopia of security topics. Topics such as privacy, SCADA and PLC security, tracking cybercriminals and the evolution of malware were discussed in depth.
Bloody Valentine For Critical Infrastructure: EtherNet/IP Exploit Could Crash Devices

Security researchers made good on a promise to release new exploits for programmable logic controllers (PLCs). The exploits include one targeting a flaw in the implementation of the EtherNet/IP (Industrial Protocol) used in many IP-enabled PLCs. The security hole, if left unaddressed, could enable a remote attacker to crash or unexpectedly reboot the devices, which are critical components of almost every industrial – and critical infrastructure installation.


The fallout from last month’s S4 Conference continues in February, with a planned Valentine’s Day release of tools that make it easy to test and exploit vulnerable programmable logic controllers and other industrial control systems. Among the releases will be a tool for cracking passwords on the common ECOM programmable logic controllers by Koyo Electronics, a Japanese firm, according to a blog post by Reid Wightman for Digital Bond.

CANCUN, MEXICO — A panel of top law enforcement officers in charge of cyber criminal investigations reveals that the guys with the white hats face an uphill climb if they want to take down cyber criminal kingpins, with outdated laws and processes on the one hand, and an increasingly skeptical and privacy-conscious public on the other.

Razvan Manole Cernaianu, perhaps better known as Tinkode, the hacker who gained notoriety after allegedly compromising a number of websites, including those of NASA, the European Space Agency, and Sun Microsystems, was recently arrested in Romania.

Verisign, the Internet security company responsible for management of the .COM domain, told federal regulators that it was the victim of several successful attacks in 2010, but that those incidents were not reported to the company’s management until September, 2011. The news was first reported by Reuters.