Hacks


Inside the 1,000 Red October Cyberespionage Malware Modules

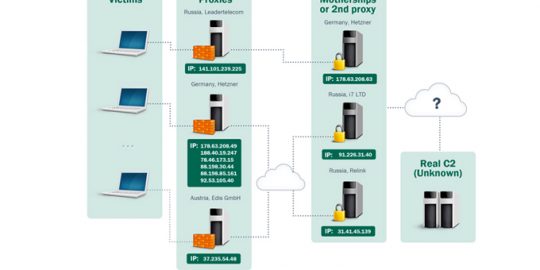
The Red October espionage malware campaign is providing security researchers with a deep dive into the complexity of targeted attacks, which in this case made use of more than 1,000 malware modules for everything from reconnaissance on targets to exfiltration of data to command and control servers.

Precision Bouncer List Phishing Kits Keep Targets Inside the Ropes

Just when you thought phishers had exhausted all avenues of innovation, a new tactic has emerged in attacks against financial institutions bringing the level of targeting and geo-filtering to precise new levels. Dubbed bouncer list phishing by RSA Security, these attack kits are built off stolen email lists that are filtered for particular targets, such as a regional bank. 


A rash of politically and socially motivated distributed denial-of-service attacks against major U.S. banks has been able to intermittently disrupt online and mobile banking services. The attackers have been able to fire unprecedented amounts of traffic at the likes of Wells Fargo, Bank of America, PNC and many others, temporarily denying customers access to their accounts online.

A 24-year-old Algerian man remains in a Thai jail awaiting extradition to the United States, where he is suspected of masterminding more than $100 million in global bank heists using the ZeuS and SpyEye Trojans.Malaysian authorities believe they’ve apprehended the hacker Hamza Bendelladj, who they say has been jetsetting around the world using millions of dollars stolen online from various banks. He was arrested at a Bangkok airport enroute from Malaysia to Egypt.