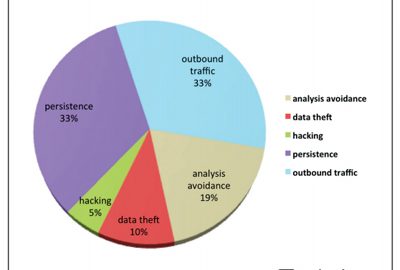
Attackers Shifting to Delivering Unknown Malware Via FTP and Web Pages
The bulk of “unknown” malware is being delivered to systems via Web-based attacks, proxies and FTP sessions, according to a study released by Palo Alto Networks this week.
The bulk of “unknown” malware is being delivered to systems via Web-based attacks, proxies and FTP sessions, according to a study released by Palo Alto Networks this week.

It appears that a spear phishing campaign was the genesis for the wiper malware infections that ultimately knocked several prominent South Korean banks and broadcasters offline last week, according to a malware analysis performed by researchers from the Finnish cybersecurity firm F-Secure.
Two message boards used by the Sanny malware as a command-and-control channel have been shut down by the Korea Information Security Agency in conjunction with security company FireEye.
Dennis Fisher talks with Wade Williamson of Palo Alto Networks about the use of compromised FTP accounts in targeted attacks and malware campaigns, and how attackers are adapting their techniques.
The Chameleon botnet continues to steal millions of dollars from online advertisers through fraudulent clicks made by malware.

The other Korea’s specter loomed large among speculators and fingers pointers Wednesday morning when reports surfaced that the networks of several prominent South Korean banks and broadcasters dropped offline.
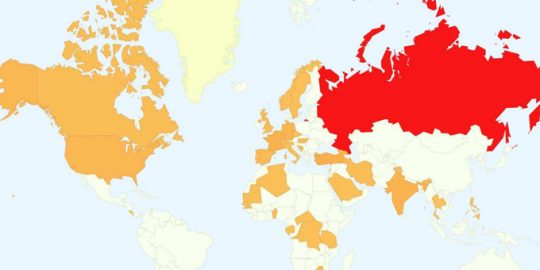
Researchers have uncovered a long-term cyber-espionage campaign that used a combination of legitimate software packages and commodity malware tools to target a variety of heavy industry, government intelligence agencies and political activists. Known as the TeamSpy crew because of its affinity for using the legitimate TeamViewer application as part of its toolset, the attackers may have been active for as long as 10 years, researchers say.

Researchers and attackers alike are quickly discovering you don’t need a fancy Java or Flash exploit to beat application sandboxes. Exploiting an unpatched kernel vulnerability in the underlying operating system, one that’s likely to stay unpatched for a long time, will do just fine.
The Ramnit malware family has been given a facelift with new anti-detection capabilities, a troubleshooting module, as well as enhanced encryption and malicious payloads.

Attackers with a control infrastructure based in China are leveraging the same vulnerability exploited by Miniduke to attack Uyghur and Tibetan activists with new exploits.
Infosec Insider content is written by a trusted community of Threatpost cybersecurity subject matter experts. Each contribution has a goal of bringing a unique voice to important cybersecurity topics. Content strives to be of the highest quality, objective and non-commercial.
Sponsored Content is paid for by an advertiser. Sponsored content is written and edited by members of our sponsor community. This content creates an opportunity for a sponsor to provide insight and commentary from their point-of-view directly to the Threatpost audience. The Threatpost editorial team does not participate in the writing or editing of Sponsored Content.


