Malware


Researchers Deconstruct Pobelka Botnet

How many inconspicuous botnets are alive and siphoning banking credentials and real money from online accounts that get little to no attention? They feast on unwitting consumers using an array of available banking Trojans to steal legitimate log-in information and sell it to the highest bidder, often with great success because they got lost in the sea of similar campaigns. Researchers at Dutch security company Fox-IT recently took apart an average botnet running amok in the Netherlands called Pobelka, a Russian word that means whitewash (perhaps a euphemism for money laundering). The analysis paints a picture of the simplicity with which even a small criminal organization can spread malware for profit, virtually unscathed.
Inside the 1,000 Red October Cyberespionage Malware Modules

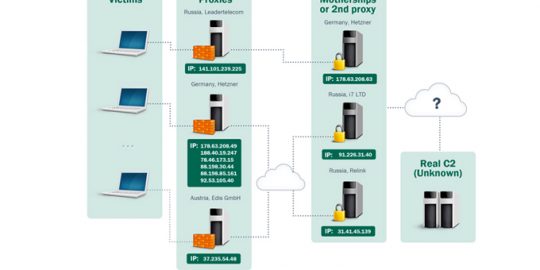
The Red October espionage malware campaign is providing security researchers with a deep dive into the complexity of targeted attacks, which in this case made use of more than 1,000 malware modules for everything from reconnaissance on targets to exfiltration of data to command and control servers.


Dennis Fisher talks with Costin Raiu and Ryan Naraine about the newly uncovered Red October cyberespionage campaign that has targeted embassies, diplomats, research facilities and military targets for more than five years now. Raiu explains the origins of the campaign, where the attackers likely are located, the complexity and scale of the malware tools involved and what other components might be lurking undiscovered out there.

In an analysis of Virut botnet samples, Symantec researchers observed the malware downloading Waledac variants, suggesting that the gangs responsible for each botnet may be cooperating with one another through some sort of affiliate program, or, at the very least, that the two threats coexist and function on single infected machines.

Oracle’s emergency Java update this weekend for a zero-day sandbox bypass vulnerability hasn’t exactly kicked off a love-fest for the company among security experts. Researchers are still cautious about recommending users re-enable the ubiquitous software, despite the availability of the fix for the latest zero-day to target the platform. 

For five years, it hid in the weeds of networks used by Eastern European diplomats, government employees and scientific research organizations, stealing data and infecting more machines in an espionage campaign rivaling Flame and others of its ilk. The campaign, called Rocra or Red October by researchers at Kaspersky Lab, focused not only on workstations, but mobile devices and networking gear to gain a foothold inside strategic organizations. Once inside, attackers pivoted internally and stole everything from files on desktops, smartphones and FTP servers, to email databases using exploits developed in China and Russian malware, Kaspersky researchers said.