Malware


Report: Toll Fraud Emerges as Android’s Number One Threat

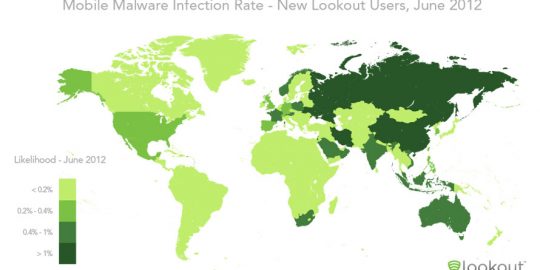
Mobile malware continues to run rampant, thanks to a growing glut of toll fraud malware – apps that have been engineered to bill its victims through premium SMS services. The malware type eclipsed spyware this year as the largest application-based threat according to mobile security firm Lookout who found it made up 79 percent of the malware it detected over the past year.

Mobile Malware Is Up – Way Up – in McAfee Q2 Threat Report

McAfee Labs researchers today announced a surge in malware samples this year – particularly threats that take advantage of mobile networks to launch drive-by downloads, control botnets using Twitter and spread ransomware that locks down infected machines and demand payments from users.


Researchers say that one of the attack groups using the two new Java zero-day vulnerabilities is the same group that was behind an earlier targeted attack campaign from 2011. That group was traced back to China and was essentially running a spear-phishing campaign, but now the crew, known as Nitro, is using the Java vulnerabilities in Web-based attacks that install the Poison Ivy remote-access tool.

There’s been a huge jump in malicious, web-based infections targeting companies in the last year, a nearly 400 percent increase from last year, according to research released today by network security company FireEye. The company’s “Advanced Threat Report – 1H 2012,” blames the jump on attackers’ ability to penetrate organizations’ usual security infrastructures.

One of the things about the investigation into the Flame malware that’s remained unclear for several months now is what ever became of the so-called Wiper virus that had been seen erasing data on machines in Iran and that led researchers to eventually discover Flame. No actual samples of Wiper have been seen, just indirect evidence that the malware existed, but now researchers have analyzed some hard drive images of machines that were affected by Wiper and found that the malware has some links to Duqu and Stuxnet, but was in fact a separate attack and doesn’t appear to have any ties to Flame.

The Air Force Life Cycle Management Center (AFLCMC) posted a broad agency announcement [PDF] recently, calling on contractors to submit concept papers detailing technological demonstrations of ‘cyberspace warfare operations’ (CWO) capabilities.

For most of the recorded history of malware, viruses, Trojans and other malicious software have been specialists. Each piece of malware typically targeted one platform, be it Windows, OS X or now, one of the mobile platforms. But the last few months have seen the rise of cross-platform malware that have the ability to infect several different kinds of machines with small variations to their code.

While researchers continue to dig into the Shamoon malware, looking for its origins and a complete understanding of its capabilities, a group calling itself the Cutting Sword of Justice is claiming responsibility for an attack on the massive Saudi oil company Aramco, which some experts believe employed Shamoon to destroy data on thousands of machines.