Spam Down 40 Percent in Rustock’s Absence
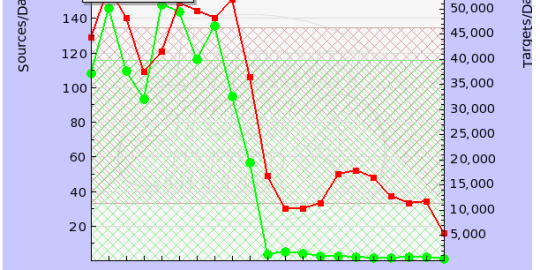
The takedown of the Rustock botnet has measurably reduced the amount of spam e-mail, according to an IBM Internet Security Systems report.
The takedown of the Rustock botnet has measurably reduced the amount of spam e-mail, according to an IBM Internet Security Systems report.
By Aleks GostevMe and Slammer (Helkern) go back a long way… to 25 January 2003 to be precise. It was a baptism of fire for me in my new role as a virus analyst at Kaspersky Lab. It was a weekend and I was alone, in charge of monitoring the incoming flow of suspicious files. I had barely been at the company a month.
There has been no respite from the tsunami of scam-emails taking advantage of the natural disaster-nuclear meltdown combo punch that is hitting Japan, according to research from Kaspersky Labs.
U.S. hosting firms accounted for the bulk of the command and control centers for the Rustock botnet, with many firms claiming that they had no idea they were harboring an illegal criminal network on their infrastructure, according to a story in Krebsonsecurity.com.
By Gunter OllmannAs a follow-up to the Rustock botnet news, Microsoft have identified themselves as the key instigators of the takedown.
This is the second time Microsoft’s legal team has been actively
involved in combating the botnet menace – and they obviously learned
from their previous attempt at trying to takedown the Waledac botnet.
RSA Security, a division of EMC Corp. has admitted that it was the victim of a sophisticated attack that resulted in the theft of secrets related to its SecurID two-factor authentication product.
Could a 16 year old girl named Kayla be the mastermind behind the breach of elite security firm HBGary?
Reports indicate that the massive drop in spam levels are linked to the sudden disappearance of the Rustock botnet. However, recent history suggests the interruption may only be temporary.
With the deadline for filing U.S. tax returns fast approaching, the U.S. Government’s watchdog agency warns that the Internal Revenue Service still hasn’t implemented steps to secure its IT infrastructure and protect taxpayers’ financial data.
Google has reacted very quickly to the news this week of a new vulnerability in Adobe Flash and on Tuesday released a new version of Chrome that includes a fix for the Flash bug. Adobe said it plans to have its own fix ready for the flaw next week.
Infosec Insider content is written by a trusted community of Threatpost cybersecurity subject matter experts. Each contribution has a goal of bringing a unique voice to important cybersecurity topics. Content strives to be of the highest quality, objective and non-commercial.
Sponsored Content is paid for by an advertiser. Sponsored content is written and edited by members of our sponsor community. This content creates an opportunity for a sponsor to provide insight and commentary from their point-of-view directly to the Threatpost audience. The Threatpost editorial team does not participate in the writing or editing of Sponsored Content.


