Malware


Siberia Exploit Kit Offers Service to Evade Anti-Malware Software

Attackers have been using legitimate online services such as VirusTotal and others to check their new pieces of malware against various security suites for some time now, but that’s become less and less effective recently. Now, the creators of some exploit kits are beginning to include less well-known, underground malware-checking services as part of their offerings to buyers of their kits.
Wikileaks Suffers Second DDoS Attack

The Wikileaks Website labored under a massive denial of service attack Tuesday, 48 hours after the site published its first installment of a massive trove of leaked U.S. diplomatic cables.Both Wikileaks.org and cablegate.wikileaks.org, the subdomain created to host the leaked U.S. embassy cables were both reachable Tuesday afternoon. However, Internet monitoring firms confirm that the site has been the target of multiple distributed denial of service (DDoS) attacks since posting the documents on Sunday.


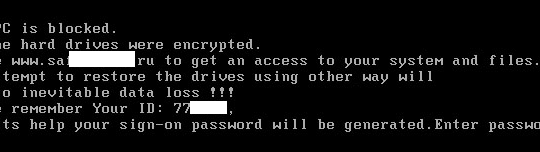
There’s a new version of the venerable GpCode ransomware attack making the rounds right now, demanding payments of $120 in order to decrypt files on infected PCs. This version, which has been active for several days now, is different from previous variants in that it overwrites the original files, preventing recovery of the data.

The Web site of Wikileaks was moving quickly to stay out of the way of large scale denial of service attacks on Sunday and Monday, following the release of a trove of sensitive U.S. diplomatic cables. The controversial site, which has spent months trying to find a home secure from government seizure, now appears to be hosted on servers that are part of U.S. firm Amazon.com’s giant hosted Web Services infrastructure based in Seattle, Washington.

China has long used the Internet’s Domain Name Service (DNS) to censor Web sites and information that the ruling Communist Party deems threatening. But now security experts warn that the government’s censorship is in danger of spilling over China’s borders: suppressing the ability of those living outside of China to find information online.

Security Worth Buying

By Dave Merkel

I’m a dirty vendor.  That
may not be the best way to start a serious dialogue about security product
effectiveness, but I hate to read a post on security theory by some insincere
tie-wearing wonk only to discover afterwards that he or she is Lord High Poobah
of Marketing at “Scaring You For Profit, Inc.” 
So I’ll just tell you who and what I am up front. I may have to wear the
tie, but I don’t have to be that guy. 
Continue at your own risk.

Exploit code is now publicly available for one of the four previously undisclosed Windows vulnerabilities that the Stuxnet worm exploits. The availability of exploit code for the Windows Task Scheduler bug used by Stuxnet makes the bug somewhat more dangerous, as there is currently no patch available for the flaw.