Mobile Security


A vulnerability exists in Samsung devices running Android version 4.1.2 that could give unauthenticated users the ability to circumvent the screen lock and view the home screen, run apps, and reach out to contacts without successfully completing Android’s pattern lock, PIN, password or Face Unlock mechanisms.

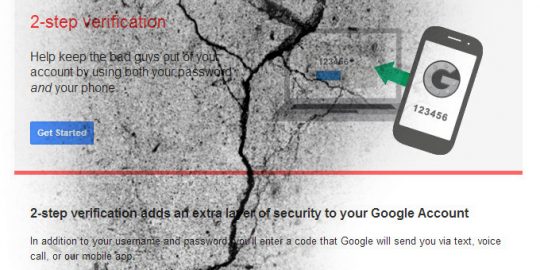
For some time, attackers had the ability to bypass Google’s two-step authentication system through access to users’ app-specific passwords, giving them full access to victims’ Google accounts, including Gmail. The vulnerability that enables this attack, discovered by researchers from DuoSecurity, has been patched by Google.

It’s getting hard to keep track of all the bugs piling up for Apple’s iPhone. Now it seems a glitch in the iOS kernel of Apple’s much maligned iOS 6.1 is responsible for yet another passcode bypass vulnerability, the second to surface this month. Attackers can apparently access users’ photos, contacts and more by following a series of steps on an iPhone running iOS 6.1.

A vulnerability exists in some components of BlackBerry mobile devices that could grant attackers access to instances of the company’s Enterprise Server (BES), according to Research in Motion (RIM), which issued an alert and released a patch for the vulnerability last week via its Knowledge Base support site. BES, the software implicated by the vulnerability, helps companies deploy BlackBerry devices.