Mobile Security


Attackers to Exploit Search Personalization, Supply Chains

Information systems and algorithms designed to personalize online search results will give attackers the ability to influence the information available to their victims in the coming years. Researchers, in turn, must seek ways to fortify these systems against malicious manipulation, according to the Emerging Cyber Threats Report 2013 [PDF], a report released ahead of yesterday’s Georgia Tech Cyber Security Summit 2012.
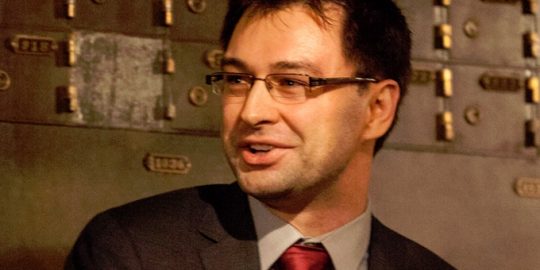
Dan Guido on the THREADS Mobile Security Conference

Dennis Fisher talks with Dan Guido, CEO of Trail of Bits and hacker-in-residence at NYU-Poly, about the school’s first mobile security conference, called THREADS, taking place this week in Brooklyn. Part of the college’s Cybersecurity Awareness Week (CSAW), THREADS will include speaker such as Dino Dai Zovi, Guido, Jon Oberheide and Vincenzo Iozzo.

Google Adds Malware Scanner to Jelly Bean 4.2

Google has been taking some steps to address the problem of malware on the Android platform in recent months, introducing the Bouncer antimalware system and some better anti-exploit technologies in Jelly Bean, the most recent version of the operating system. Now, the company is implementing some additional security features designed to protect users from malicious apps and malware that tries to send premium-rate SMS messages.


Yes. You read that headline correctly. F-Secure is talking about the beleaguered and nearly defunct Symbian operating system, upon which Nokia halted nearly all development in February before announcing that it had been put in maintenance mode in September. Despite a nearly 63 percent drop in shipments of Symbian devices in the second quarter of this year and its modest 4.4 percent share of the global smartphone market, Symbian was the new home for 21 variants of malware in Q3, up 17 percent from Q2.

A vulnerability discovered in the Android Open Source Project enables malicious applications to send SMS messages without user permission across all recent Android platforms.While no exploits are active in the wild, one could be built that could be at the center of various SMS phishing, or smishing, attacks, said Xuxian Jiang, associate professor in the North Carolina State University computer science department.

Older versions of Broadcom firmware found in a number of mobile devices from major vendors including the Apple iPhone, iPad, Samsung Galaxy S and HTC Droid Incredible are vulnerable to a denial of service attack.Researchers Andres Blanco and Matias Eissler of Core Security Technologies reported the vulnerability in August, and this week published details on proof-of-concept exploit code.

CyanogenMod, a popular open source firmware replacement for Android phones, has patched a hole in its code that was locally logging swipe gestures used to unlock phones. The problem, which stemmed from a line of code that was never intended for release, was fixed in an update posted for download on the firmware’s review site earlier this week.

A new report from Trend Micro showed a 483 percent jump in malware — including “aggressive adware” that harvests person data without permission using legitimate ad networks.It’s no surprise that the open nature of the Android platform makes it a magnet for malware, but the type of malware becoming more prevalent illustrates the blurring lines between legitimate apps that gather data for company use and those that violate users’ privacy.

There are thousands of apps in the Google Play mobile market that contain serious mistakes in the way that SSL/TLS is implemented, leaving them vulnerable to man-in-the-middle attacks that could compromise sensitive user data such as banking credentials, credit card numbers and other information. Researchers from a pair of German universities conducted a detailed analysis of thousands of Android apps and found that better than 15 percent of those apps had weak or bad SSL implementations.