Double-Stuffed: Dunkin’ Hit by Another Credential-Stuffing Attack
Dunkin’ Donuts’ loyalty program was hit with a credential stuffing attack that targeted names, email addresses, 16-digit DD Perks account numbers and DD Perks QR codes.
Dunkin’ Donuts’ loyalty program was hit with a credential stuffing attack that targeted names, email addresses, 16-digit DD Perks account numbers and DD Perks QR codes.

In its February Patch Tuesday bulletin Microsoft patches four public bugs and one that under active attack.

Wyden and Rubio are eyeing VPN services they say could be instruments of espionage for Russia and China.

Three major websites are making data-privacy news this week.
Researchers theorize how Bezos’ very personal pictures may have been allegedly hacked.

Today’s financial cyber-rings have corporate insider and management roles — cybercrime is not just just for hackers and coders anymore.

Flaws in this connected smart scale might give the diet-challenged a legitimate reason to be nervous.
The children’s smartwatch allows bad actors to track their location and communicate with them, according to the alert.
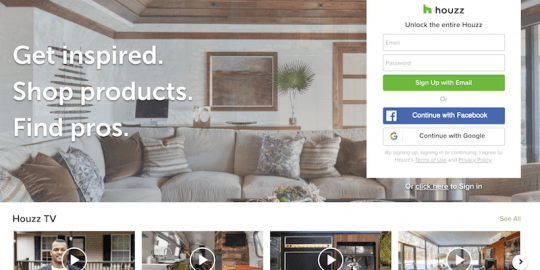
The decorating website said that account usernames, passwords and more have been compromised as part of a breach.
Scams, infrastructure attacks, data harvesting and attacks on streamers are all in the offing.
Infosec Insider content is written by a trusted community of Threatpost cybersecurity subject matter experts. Each contribution has a goal of bringing a unique voice to important cybersecurity topics. Content strives to be of the highest quality, objective and non-commercial.
Sponsored Content is paid for by an advertiser. Sponsored content is written and edited by members of our sponsor community. This content creates an opportunity for a sponsor to provide insight and commentary from their point-of-view directly to the Threatpost audience. The Threatpost editorial team does not participate in the writing or editing of Sponsored Content.


