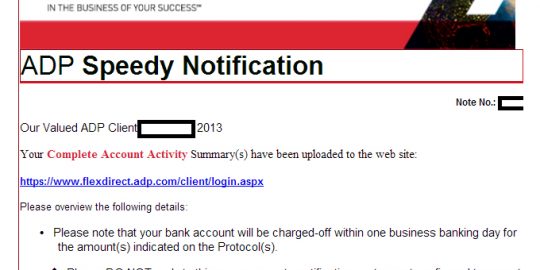
ADP-Themed Phishing Emails Lead to Blackhole Sites
Scammers are spamming out malicious emails purporting to come from payroll processing company ADP, according Dancho Danchev of Webroot.
Scammers are spamming out malicious emails purporting to come from payroll processing company ADP, according Dancho Danchev of Webroot.
Working with forensics experts from the FBI, Ernst & Young’s Fraud Investigation and Dispute Services Practice developed a piece of linguistic, fraud-monitoring software that identified language commonly used among employees engaged in corporate malfeasance. The accounting giant plans to offer their newly developed fraud-detection capacity as a service to their clients.
An Idaho non-profit hospice has been fined $50,000 for losing a laptop containing unencrypted data on 441 patients.The laptop was stolen in February 2011 from a hospice worker’s car and never retrieved, according to news accounts. But Hospice of North Idaho officials say there is no evidence the personal information has been used to commit identity theft or fraud.

In the last two years, 94 percent of healthcare organizations that took part in the Ponemon Institute’s “Third Annual Benchmark Study on Patient Privacy & Data Security” [PDF] reported that they had suffered at least one data breach; 45 percent reported that they had been the victim of at more than five data breaches.
UPDATE – Some 4,000 University of Michigan Health Systems patients had their medical data compromised last month when a vendor’s laptop containing medication log files was stolen from a vehicle.That medication management provider, Mountain View, Calif.-based Omnicell, admits it violated both its own and UMHS hospitals’ data storage policies when it left patients’ demographics, medication regimes and admissions records on an unsecured device that was stolen from an Omnicell employee’s car on Nov. 14.
Apple shipped fixes for nine vulnerabilities in its QuickTime multimedia platform. The QuickTime 7.7.3 update resolves bugs for Windows 7, Vista, and XP service pack 2 and later.
Medi-Cal, California’s Medicaid welfare program, came clean to customers this week admitting it mistakenly posted almost 14,000 of its users’ Social Security numbers online last month.
An estimated 1.1 million consumers are at risk of identity theft after thieves broke into servers belonging to Nationwide and Allied insurance companies. Victims include current policyholders and those who sought insurance quotes.The breach took place Oct. 3 and was discovered the same day. Nationwide immediately contacted authorities, but it waited to inform consumers directly. Earlier news accounts offered some hints at the scope of the breach, including some 30,000 victims in Florida and Ohio and 90,000 in Iowa.
Small physician practices, much like their small commercial business counterparts, have been the primary source of health care related data breaches, according to an analysis of breaches from 2009 to October 2012 released today by the Health Information Trust Alliance (HITRUST).

Persistent targeted attacks against the government, financial services, manufacturing and critical infrastructure take on many characteristics. Attackers can have different backgrounds and motivations, and the tools they use can range from commodity malware to zero-day exploits.
Infosec Insider content is written by a trusted community of Threatpost cybersecurity subject matter experts. Each contribution has a goal of bringing a unique voice to important cybersecurity topics. Content strives to be of the highest quality, objective and non-commercial.
Sponsored Content is paid for by an advertiser. Sponsored content is written and edited by members of our sponsor community. This content creates an opportunity for a sponsor to provide insight and commentary from their point-of-view directly to the Threatpost audience. The Threatpost editorial team does not participate in the writing or editing of Sponsored Content.


