
Cisco Patches DoS, Buffer Overflow Vulnerabilities in UCM
Cisco has fixed several vulnerabilities that if left unpatched could lead to a denial of service attack and allow attackers to modify data or execute arbitrary commands, among other problems.
Cisco has fixed several vulnerabilities that if left unpatched could lead to a denial of service attack and allow attackers to modify data or execute arbitrary commands, among other problems.

The Food and Drug Administration (FDA) last week issued a series of guidelines regarding the regulation of radio frequency (RF) technology in medical devices, moves that if put into practice, could eventually help shore up the increasingly vulnerable medical device security world.

There are 25 fresh security patches in the newest version of Google Chrome, including fixes for a number of high-severity vulnerabilities. Chrome 29 also includes a number of performance enhancements.
An attacker, who may have gotten the information from the database of a third party, claims to have access to the OAuth login tokens and secrets for every Twitter user. He has posted more than 15,000 of the entries online and claims that he can now access the account of any user he wishes. Twitter officials, however, say no accounts have been compromised.
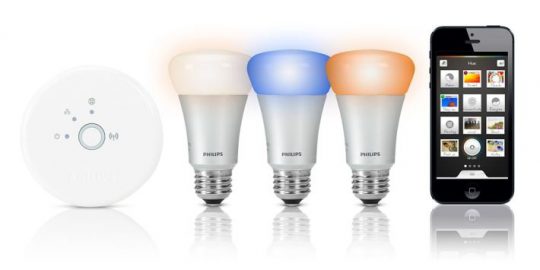
According to research unveiled this week some types of web-enabled light bulbs are vulnerable to a flaw wherein an attacker could literally leave users of the bulbs in the dark.
A vulnerability in the BIND domain name system (DNS) software could give an attacker the ability to easily and reliably control queried name servers chosen by the most widely deployed DNS software on the Internet, according to new research presented at the Woot Conference in Washington D.C. today.
Content management system Joomla patched a zero-day vulnerability that allowed attackers to upload malicious code that led victims to the Blackhole exploit kit.

Google’s bug bounty program has been one of the more successful reward systems of its kind, and the company has regularly modified and expanded the program over the years to keep pace with what’s going on in the industry. Google also has increased the rewards it offers for certain kinds of vulnerabilities several times, and the company is doing it again, raising the lower reward level from $1,000 to $5,000.

Dennis Fisher and Mike Mimoso discuss the news from Black Hat and DEF CON, particularly the fact that the Web seems to be broken and that a lot of the attacks revealed in Las Vegas don’t have easy solutions.
Here’s an idea: stop fixing every vulnerability you read about. The best thing to do, it turns out, is to look at the vulnerabilities that are in both Metasploit and the Exploit Database and fix those. That gives you the highest chance of fixing bugs that are likely to be used in an actual attack.
Infosec Insider content is written by a trusted community of Threatpost cybersecurity subject matter experts. Each contribution has a goal of bringing a unique voice to important cybersecurity topics. Content strives to be of the highest quality, objective and non-commercial.
Sponsored Content is paid for by an advertiser. Sponsored content is written and edited by members of our sponsor community. This content creates an opportunity for a sponsor to provide insight and commentary from their point-of-view directly to the Threatpost audience. The Threatpost editorial team does not participate in the writing or editing of Sponsored Content.


