Vulnerabilities


Researcher Warns of D-Link Router Vulnerabilities

A combination of vulnerabilities in D-Link’s DIR-300 and DIR-600 routers could allow an attacker to inject arbitrary shell commands and ultimately compromise the device, according to German security researcher Michael Messner who publicly disclosed the flaw on his personal blog Monday.


A number of security vulnerabilities were repaired in the latest version of the Opera browser, which was released today. However, a security researcher says that users who downloaded the browser from Apple’s Mac App Store won’t have access to version 12.13; in fact you’ll be two revs behind as of today.Graham Cluley of Sophos reported today that Opera 12.11 is the latest version available at the Mac App Store. Version 12.12 was released Dec. 18.

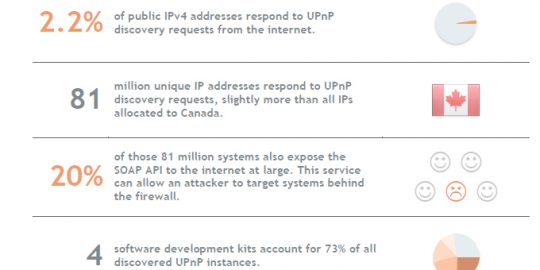
In a project that found more than 80 million unique IP addresses responding to Universal Plug and Play (UPnP) discovery requests, researchers at Rapid7 were shocked to find that somewhere between 40 and 50 million of those are vulnerable to at least one of three known attacks.

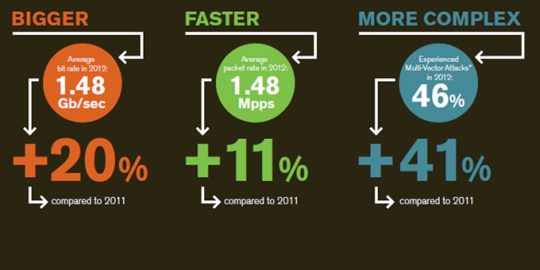
Back in the dark days of dial-up connectivity, attackers wouldn’t bother compromising home computers as bots to be used in distributed denial-of-service. The lack of bandwidth made PCs persona non grata in the DDoS world. Instead, attackers targeted Web servers, the only machines with the high-speed broadband connections to make DDoS viable.In the years since, broadband has literally come home and personal machines have been compromised by the millions for everything from spam to flood attacks against websites and online services.