Google Launches New Privacy Policy to Worldwide Criticism
Search giant Google rolled out a sweeping new privacy policy on Thursday, despite continuing opposition from countries in Europe and Asia to the changes.
Search giant Google rolled out a sweeping new privacy policy on Thursday, despite continuing opposition from countries in Europe and Asia to the changes.
SAN FRANCISCO–The PCI DSS standard has taken a beating from critics, security experts and CSOs virtually since the day it appeared in its earliest form in 2004. It’s evolved quite a bit in the intervening years, but it hasn’t shaken any of that criticism, and security folks say there’s a good reason for that: a PCI-compliant network is no real hurdle to exploitation.
The EFF has released a new version of its HTTPS Everywhere browser extension, and users can now turn on a feature that will send the EFF copies of digital certificates that the browser encounters, allowing the organization to look for flawed, fake or expired certificates.
by B.K. DeLongWikileaks’ decision this week to post the first of five million emails from Texas-based strategic intelligence firm Stratfor shone a spotlight on what experts say is a serious and growing problem: lax data, network and physical security at third party vendors and service providers. But organizations that think they can wash their hands of the security mess caused by business partners and contractors may be in for a rude awakening.
A new attack against online banking customers uses a malware platform to trick its victims into verifying bogus transactions.The attack, first described by Trusteer CTO Amit Klein, waits for an unsuspecting business banking customer to log online before telling them that “security checks” need to be performed.
PayPal announced that it is changing both its privacy and user agreement policies, adding tweaks to its customer identification program and the way it collects and stores its customers’ personal information. The changes will take effect on April 1.
Right on cue this week, the anarchic hacking collective Anonymous stepped up and grabbed the story line away from the lions of the IT security industry.With the annual RSA Conference set to begin, the whistle blowing site Wikileaks released the first of some five million e-mail messages stolen from the security intelligence firm Stratfor. Ever sensitive to the fickle attention of the media, Anonymous inserted itself into the story, claiming responsibility for leaking the data and pointing a finger of blame at Stratfor and its media, private and public sector customers, which Anonymous accuses of spying and other dark offenses.
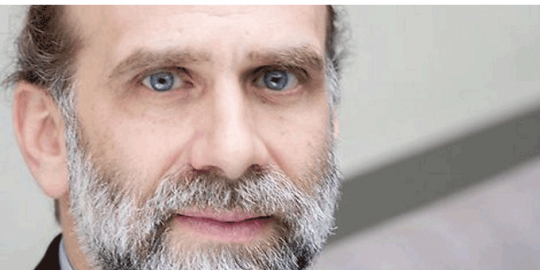
Dennis Fisher talks with cryptographer and author Bruce Schneier about his new book, Liars and Outliers, the role of trust in society and security, the ways in which technology helps promote trust and how various groups and actors defect the norm and take advantage of that trust.
According to a request for proposals from the government’s National ICT (Information and Communications and Technologies) R&D Fund, the government is struggling to stay on top of growing Internet and WEb use and is looking for a way to filter out undesirable Web sites.

The Obama administration today unveiled a new consumer-privacy plan designed to help better protect users’ rights online, including a privacy “bill of rights” that spells out exactly what consumers should expect from the companies they work with online. In conjunction with this new initiative, Google has said that it finally will add the do-not-track button to its Chrome browser.
Infosec Insider content is written by a trusted community of Threatpost cybersecurity subject matter experts. Each contribution has a goal of bringing a unique voice to important cybersecurity topics. Content strives to be of the highest quality, objective and non-commercial.
Sponsored Content is paid for by an advertiser. Sponsored content is written and edited by members of our sponsor community. This content creates an opportunity for a sponsor to provide insight and commentary from their point-of-view directly to the Threatpost audience. The Threatpost editorial team does not participate in the writing or editing of Sponsored Content.


