Web Security


Lessons From the Rustock Takedown

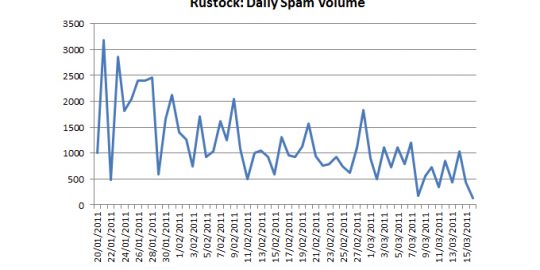
By Gunter OllmannAs a follow-up to the Rustock botnet news, Microsoft have identified themselves as the key instigators of the takedown.
This is the second time Microsoft’s legal team has been actively
involved in combating the botnet menace – and they obviously learned
from their previous attempt at trying to takedown the Waledac botnet.
Threatpost News Roundup on ITEC This Week

It was a big week in security, what with the takedown of the Rustock botnet takedown, there was a major attack against security firm RSA Security. Threatpost Editor Paul Roberts had a chance to sit down with Bill Sell, host of the weekly IT security news show ITEC This Week on the Pulse Network. Paul and Bill talk about the week’s events, and do a round up of the recent RSA Security Conference.

Greg Hoglund Discusses HBGary Mishap

Greg Hoglund, CTO of HBGary, admits that lackluster security played a central role in the breach that led to the release of some 50,000 company emails, but also disputes common understanding and reported details of the hack, going so far as to say there was actually no hack at all.


Dennis Fisher talks with Alex Lanstein of FireEye about this week’s takedown of the Rustock botnet, the important legal precedent it helped set with Microsoft’s lawsuit and the mechanics behind the operation and dismantling of large-scale botnets.

The DNS Security Extensions (DNSSEC) will be equipped for the “.com” entity by March 31, according to a PCMag.com report.While DNSSEC enhances DNS security as it is, the newly added .com security will act as an extra layer of protection, according to according to Matt Larson, the Vice President of DNS Research at Verisign.

With the deadline for filing U.S. tax returns fast approaching, the U.S. Government’s watchdog agency warns that the Internal Revenue Service still hasn’t implemented steps to secure its IT infrastructure and protect taxpayers’ financial data.

Twitter has changed the way that users access the company’s main site, now giving them the option to enable HTTPS by default, forcing a secure connection for most interaction with the service. However, the change does not apply to all of the popular apps users employ to access Twitter on smartphones and other devices.

A new, detailed analysis of the operations of the infamous Cutwail/Pushdo botnet shows that the network, which had been he target of several takedown attempts in the last couple of years, is not only amazingly resilient, but also is incredibly prolific, with one section of the botnet sending more than 1.7 trillion spam messages, and quite profitable, generating as much as $4 million in profits for its owners.