Dennis Fisher

About

Dennis Fisher is a journalist with more than 13 years of experience covering information security.

Fake AT&T Emails Using Blackhole Exploit Kit to Install Malware

For the last few weeks there have been a series of quite authentic-looking phishing emails making the rounds, purporting to come from AT&T and informing the recipient that their bill is ready to view. The emails look nearly identical to a real bill and researchers say that users who fall for the ruse are going to be rewarded with a redirection to a site hosting the Blackhole exploit kit.


Dennis Fisher talks with Joe Stewart of the Dell SecureWorks Counter Threat Unit about his team’s new research on the landscape of APT malware families, who is behind the use of these tools and how poorly prepared most organizations are for attacks by these crews.

Officials at Huawei Technologies say that they’re looking into claims by security researchers made at DEF CON last week that there are a handful of serious security vulnerabilities in some of the company’s routers. Saying it employs “rigorous security strategies and policies” Huawei is trying to verify the flaws discovered by researchers Felix “FX” Lindner and Gregor Kopf.

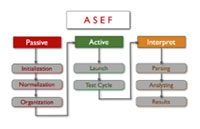
A researcher at Qualys has released a new tool designed to allow users–even non-technical ones–to evaluate the security and behaviors of the apps installed on their Android devices. Known as the Android Security Evaluation Framework, the tool not only looks at the general security of an app, but also at what kind of data the app is collecting and what it’s doing with that information.

A British teenager has been sentenced to six months in jail after pleading guilty to illegally accessing the Gmail account of a former top aide to former Prime Minister Tony Blair. Junaid Hussain was allegedly a member of the TeamPoison hacking crew and had posted some of Blair’s personal information online after the attack.

Attackers and malware writers, like many other people, tend to specialize, honing their skills in one particular discipline in order to maximize their chances for success. But Microsoft researchers have come across a series of malware samples and exploits that show that some attackers are beginning to target the same vulnerability across multiple platforms as a way to make the most out of their efforts.

LAS VEGAS–Here’s something that you might not know about RIM: it has a rather large security response and research team. The maker of the BlackBerry phones–once the must-have fashion accessory for executives and Barack Obama–historically has been almost silent on the way that it handles product security and vulnerabilities. But that’s beginning to change, in large part perhaps because the security response team at RIM is full of veterans of Microsoft’s Security Response Center, who learned the value of communication the hard way.