Ryan Naraine

SMB2 Exploit Fitted into Metasploit; Attacks Likely

Fully functional exploit code for the (still unpatched) Windows SMB v2 vulnerability has been released to the public domain via the freely available Metasploit point-and-click attack tool, raising the likelihood for remote in-the-wild code execution attacks.
The exploit, created and released by Harmony Security’s Stephen Fewer, provides a clear roadmap for hackers to plant malware or open backdoors on Windows Vista Service Pack 1 and 2 as well as Windows 2008 SP1 server.

Botnet Hiding Commands as JPEG Images

Security researchers have stumbled on a new botnet that uses an interesting technique to mask its nefarious intentions.
The Monkif/DIKhora botnet, which is pushing out Trojan downloaders to infected machines, is encoding the instructions to appear as if the command-and-control server is returning a JPEG image file, according to SecureWorks researcher Jason Milletary.  Read the full story [secureworks.com]

BlackBerry Dinged by Phishing Flaw

Research in Motion (RIM) has shipped a fix for a serious security vulnerability that exposes BlackBerry users to phishing attacks.
The certificate handling vulnerability, which carries a CVSS severity score of 6.8, affects all versions of the BlackBerry device software. 


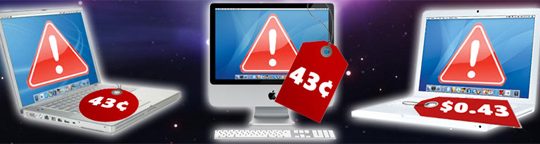
GENEVA — In a sign that cyber-criminals are investing more time and resources into attacks against Apple’s Mac users, a new malware affiliate program has been discovered offering 43c for every infected Mac machine.
During an eye-opening presentation at the VB Conference 2009 conference here, Sophos Labs researcher Dmitry Samosseikko provided a glimpse into the “Partnerka,” a Russian network of spam and malware affiliates that have turned their attention to the Mac platform — using social engineering tricks to load fake codecs and scareware programs.

Cyber-criminals are using interest in MMS or SMS on the iPhone to trick users into downloading rogue antivirus software.
According to security company Websense, attackers are abusing Google’s search engine to get users to click on links leading to a malicious page pushing scareware.  Read the full story [eweek.com]

The IDG News Service is reporting on a new FBI investigation [computerworld.com] of a rash of online hacking attacks and bank robberies against school districts in Illinois.

FBI investigators are working on a computer intrusion case at the Crystal Lake School District in Crystal Lake, Illinois, said Ross Rice, a spokesman with the FBI’s Chicago office. But several other school districts also believe that they have been hit by the same malicious software, Rice said.  The Clampi malware family [secureworks.com] may  be linked to these attacks.

In the never-ending battle to protect computer networks from intruders, security experts are deploying a new defense modeled after one of nature’s hardiest creatures — the ant.
Unlike traditional security devices, which are static, these “digital ants” wander through computer networks looking for threats, such as “computer worms”  — self-replicating programs designed to steal information or facilitate unauthorized use of machines. When a digital ant detects a threat, it doesn’t take long for an army of ants to converge at that location, drawing the attention of human operators who step in to investigate.  Read the full story [wfu.edu]

Google’s decision to introduce a plug-in that runs Google Chrome inside Microsoft’s Internet Explorer isn’t sitting well with the folks at Redmond.
The Google Chrome Frame, which is presented as a  seamless way to bring Google Chrome’s open web technologies and speedy JavaScript engine to Internet Explorer, has increased the attack surface for IE users, Microsoft said today.

On the heels of yet another Twitter phishing attack, Threatpost editor Ryan Naraine chats with Kaspersky Lab malware researcher Costin Raiu about a new "Krab Krawler" project that pinpoints signs of malicious activity on Twitter.  Raiu introduced the project at this year’s Virus Bulletin conference.  View the VB presentation here.

Cisco has released a peck of patches to cover multiple security flaws in its flagship Cisco IOS (originally Internetwork Operating System), warning that the bugs exposes businesses to denial-of-service or policy bypass attacks.
In all, the networking vendor released 10 advisories covering Cisco IOS flaws and a separate alert for a vulnerability in the Cisco Unified Communications Manager. Read the Cisco advisory bundle [cisco.com].