Ryan Naraine

‘Highly Critical’ Bug Bites Firefox 3.5

Exploit code for a “highly critical” vulnerability in Mozilla Firefox has been released on the Internet, putting millions of Web surfers at risk of remote code execution attacks.
The vulnerability is currently unpatched, according to an advisory from Secunia.
How to Plan for Smartphone Security in the Enterprise

From eWEEK (Chris De Herrera)
One of the major challenges CIOs face is the deployment and security of smartphones in the enterprise. It’s important for CIOs to assess how their organization should secure the smartphones employees use to access corporate resources. Here, Knowledge Center contributor Chris De Herrera explains how CIOs can deal with some common security concerns regarding smartphones deployed in the enterprise, including Apple iPhone, RIM BlackBerry, Windows Mobile, Google Android and Palm Pre devices.  Read the full story [eweek.com]

Twitter Suspends Accounts of Users With Infected Computers

From IDG News Service (Jeremy Kirk)
Twitter is suspending the accounts of some users whose computers have fallen victim to a well-known piece of malicious software that has targeted other sites such as Facebook and MySpace.
The malware, Koobface, is designed to spread itself by checking to see if person is logged into a social network. It will then post fraudulent messages on the person’s Twitter account trying to entice friends to click the link, which then leads to a malicious Web site that tries to infect the PC.  Read the full story [computerworld.com]


As night follows day, malicious hackers are following high-profile news around celebrity deaths to launch attacks.

According to a warning from the U.S. Computer Emergency Response team, there are several spam campaigns, phishing attacks, and malicious code targeting the recent deaths of Michael Jackson and Farrah Fawcett.

From The New York Times (Riva Richmond)
Facebook launched a beta test today that foreshadows new privacy controls coming to “Publisher” – the box at the top of your home and profile pages where you add content. The changes will let you easily specify who among your friends gets to see that specific photo, video or status update you’re sharing. Read the full story [nytimes.com]

From CERT (Will Dormann)

Two recent US-CERT Vulnerability Notes [cert.org] describe similar issues in the Adobe Reader and Foxit Reader PDF viewing applications. The vulnerabilities, that both applications failed to properly handle JPEG2000 (JPX) data streams, were discovered as part of our Vulnerability Discovery initiative. The two vulnerability notes are quite similar, except for one aspect: attack surface.  Read the full blog post [cert.org]

From SearchSecurity 

Network security researcher Dan Kaminsky has had a year to reflect on the impact of the cache poisoning vulnerability he discovered in the Domain Name System (DNS). Kaminsky revealed during last year’s Black Hat Briefings a technique that made it relatively easy to exploit the bug and enable an attacker to redirect website requests to malicious sites. In the time since, Kaminsky has become an advocate for improving security in DNS, and ultimately, trust on the Internet.  In this interview, Kaminsky talks about how the implementation of DNSSEC would enable greater security and trust on the Net and provide a platform for the development of new security products and services. Read the full interview [techtarget.com]

From IDG News Service (Robert McMillan)
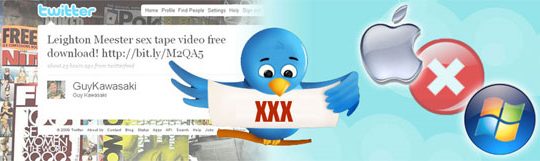
Former Apple Macintosh evangelist Guy Kawasaki posts Twitter messages about a lot of different thing, but the message he put up Tuesday was really out of character: “Leighton Meester sex tape video free download!”
His message included a link that, after some further clicking, landed Kawasaki’s followers on a fake porn site where online criminals try to install a nasty Trojan horse program on victim’s computers. And in an interesting twist, the program attacks both Mac and Windows users.  Read the full story [computerworld.com]

From IDG News Service (Stephen Lawson)
Alan Ralsky, a spam kingpin who was convicted of felony bank fraud in 1995, could face more than seven years in prison after pleading guilty in a stock fraud case involving spam messages that pumped up Chinese “penny” stocks.
Ralsky and four other individuals pleaded guilty on Monday, joining three others who had pleaded guilty earlier, the U.S. Department of Justice announced Monday. Cases are still pending against three other people, they said. The defendants were indicted in the Eastern District of Michigan in 2007. Read the full story [pcworld.com]

From SearchSecurity.com (Robert Westervelt)
The dismal economy has put the brakes on a lot of security projects, but the need to maintain the basics and automate some security functions has fueled interest in managed security services and some specific security areas, according to analysts at Gartner Inc.
Despite the dour economy, core security software functions are on pace to continue to grow, said Adam Hils, a principal research analyst with Gartner Research. Antivirus, antimalware and email security will continue to gain interest. New projects will be driven by regulatory compliance initiatives and areas affected by cost cutting measures. Read the full story [techtarget.com]