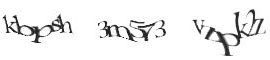
Ryan Naraine

Cybergangs use cheap labor to break codes on social sites

From USA Today (Byron Acohido)
It’s become the new front in cybercrime: scams and identity-theft programs that attack e-mail accounts and users of social-networking sites such as Facebook and MySpace.
To carry out many of these automated attacks, cybercriminals first must overcome “captchas,” the distorted letters and characters that users of an e-mail or social-networking account are required to type to complete certain online forms. For years, captchas have helped to stop or bog down automated programs aimed at creating, among other things, e-mail accounts that promote scams such as fake computer virus protection and bogus accounts on social websites that can be used to collect personal information on legitimate users.

Will there be a digital Pearl Harbor?

Will there be one major catastrophe, or just smaller disasters? Panelists discuss what security issues we should be watching out for, where the threat might come from, and the difficulties in predicting the unpredictable. (Via ZDNet)

NKill aims to catalog vulnerabilities of every computer

From IDG News Service (Sumner Lemon) 
A security consultant is developing a search engine called NKill that aims to track the security vulnerabilities on every computer connected to the Internet, with the ability for users to search for vulnerable computers in a country or inside a specific company.
NKill, which currently covers all .com, .org and .net domain names, will be made available to the public within one month or so, said Anthony Zboralski, founder of Bellua Asia-Pacific, speaking Wednesday at the Hack In The Box Security Conference in Dubai. Read the full story [networkworld.com]


From ZDNet (Dancho Danchev)
PandaLabs is reporting on a newly discovered ransomware variant [pandasecurity.com]which locks the affected user’s PC, and demands a premium SMS in order to deactivate it.
The ransomware doesn’t have any self-propagation functions and appears to be coming under the form of a typical fake codec that has been affecting users for over a week now. The message (in Russian) demands that the affected user sends an SMS with the pseudo-unique number to the given number in order to receive deactivation code. Read the full story [zdnet.com]

From DarkReading (Kelly Jackson Higgins)
Danish security firm Secunia is attempting to rally other software vendors to develop an industry-standard tool that automatically updates all applications on a consumer’s PC.
Secunia envisions an industry-standard app that runs when a laptop starts up, for example, scanning for unpatched or vulnerable apps and guiding the user with simple point-and-click options to update the machine. Read the full story [darkreading.com]

Mozilla has shipped a refresh [mozilla.com] of its flagship Firefox browser to fix a dozen documented vulnerabilities that expose users to URL spoofing, cross-site scripting, code injection and code execution attacks.
The most serious fix covers four browser engine and JavaScript engine crashes where Mozilla’s developers found evidence of memory corruption.  Read the full story [zdnet.com]

From The Register (Dan Goodin)

One of Brazil’s biggest banks has suffered an attack that redirected its customers to fraudulent websites that attempted to steal passwords and install malware, according to an unconfirmed report.

According to this Google translation of an article penned in Portuguese, the redirection of Bradesco was the result of what’s known as a cache poisoning attack on Brazilian internet service provider NET Virtua. Read the full story [theregister.co.uk]

From PC Advisor (Carrie-Ann Skinner)

More than 80 percent of websites that had been poisoned with malicious code between 2008 and 2009 were removed within 24 hours, says AVG.

The security vendor’s Web Threat Profile Report estimated that on any one day between 8 and 14 million web users are being exposed to social engineering scams, such hoax Facebook pages or rogue security apps that encourages surfers to download malicious software to their PC. Read the full story [cio.com]

From The H Security
Research In Motion have published an advisory [blackberry.com] to warn of another vulnerability in the PDF distiller of the BlackBerry Attachment service. This new vulnerability is in addition to previous issues with the PDF distiller service.
According to US-CERT, the issue is related to VU196617 [cert.org], which involves the open source Xpdf and poppler applications and their handling of JBIG2 data. Read the full story [h-online.com]

From CIO (Joan Goodchild)
You can install the best firewalls, patch religiously, and make sure your anti-virus software is always up-to-date, but there is one online risk factor you can never control: the user. Whether they are downloading dangerous content or falling prey to phishing scams, the end user continues to be the toughest security risk to mitigate in most organizations.
With that constant struggle in mind, giving users education about what they are doing and why it is dangerous is the more effective strategy. Here are some of the more common security missteps users take and some advice [cio.com] on how to stay secure online.