Malware


Phishing Sites, Rogue AV Skyrocket in 2009

From SearchSecurity.com (Robert Westervelt)

Phishing websites and rogue antivirus programs increased precipitously in the first half of 2009, according to a new report issued by the Antiphishing Working Group. The number of unique phishing websites reached a high of nearly 50,000 in June, the second highest on record since more than 55,000 phishing websites were recorded in April, 2007. Read the full story [SearchSecurity.com].
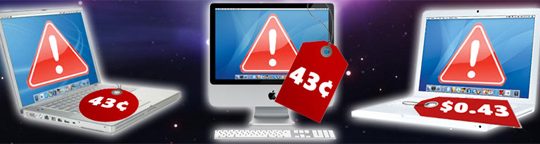
Apple Malware Bounty: Infect a Mac, Earn $0.43

GENEVA — In a sign that cyber-criminals are investing more time and resources into attacks against Apple’s Mac users, a new malware affiliate program has been discovered offering 43c for every infected Mac machine.
During an eye-opening presentation at the VB Conference 2009 conference here, Sophos Labs researcher Dmitry Samosseikko provided a glimpse into the “Partnerka,” a Russian network of spam and malware affiliates that have turned their attention to the Mac platform — using social engineering tricks to load fake codecs and scareware programs.

iPhone SMS Used as Bait in Rogue AV Scam

Cyber-criminals are using interest in MMS or SMS on the iPhone to trick users into downloading rogue antivirus software.
According to security company Websense, attackers are abusing Google’s search engine to get users to click on links leading to a malicious page pushing scareware.  Read the full story [eweek.com]


On the heels of yet another Twitter phishing attack, Threatpost editor Ryan Naraine chats with Kaspersky Lab malware researcher Costin Raiu about a new "Krab Krawler" project that pinpoints signs of malicious activity on Twitter.  Raiu introduced the project at this year’s Virus Bulletin conference.  View the VB presentation here.

From IDG News Service (Robert McMillan)
Criminals flooded several online ad networks with malicious advertisements over the weekend, causing popular Web sites such as the Drudge Report, Horoscope.com and Lyrics.com to inadvertently attack their readers, a security company said Wednesday.
The trouble started on Saturday, when the criminals somehow placed the malicious ads on networks managed by Google’s DoubleClick, as well as two others: YieldManager and ValueClick’s Fastclick network.  Read the full story [computerworld.com]

Some sections of the popular PBS.org Web site have been hijacked by hackers serving up a cocktail of dangerous exploits.
According to researchers at Purewire, attempts to access certain PBS Web site pages yielded JavaScript that serves exploits from a malicious domain via an iframe.

An ongoing attack on Google users is sending victims to rogue anti-virus software sites, researchers said this week.
The attack takes advantage of Google’s page-ranking feature, according to researchers at eSoft’s Threat Prevention Team. The scam works like this: An attacker hacks a site, but instead of embedding exploits on the hacked site, they put links to other websites to boost rankings for malicious sites, and Google users in particular seem to be the targets. Read the full story [scmagazineus.com]

Gamers trying to update their mouse or keyboard drivers from accessory maker Razer USA’s Web site recently may have gotten more than they bargained for.
According to the IDG News Service, the company’s computers appear to have been hacked, and its support site used to spread malicious Trojan horse programs.  Customers who downloaded Razer software would get the drivers they requested, but they also got an obscure Trojan program.