Malware


Google to Address Malicious Ads at Virus Bulletin

There are security conferences, and then there is Virus Bulletin. While virtually all of the presentations are from researchers working at antimalware vendors and other security companies, the talks are quite technical and this year’s conference, which starts Wednesday in Geneva, Switzerland, features one most interesting speaker: Eric Davis of Google.
A Peek at the ‘Bahama’ Click Fraud Botnet

A new botnet, codenamed the ‘Bahama’ botnet has been linked to the recent surge in click-fraud and scareware attacks.  This video by researchers at Click Forensics shows the Bahama Botnet in action.  More on this botnet in this report.

Remote exploit released for Windows Vista SMB2 worm hole

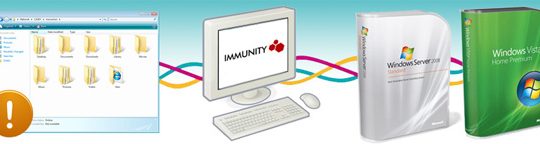
Security researchers at penetration testing firm Immunity have created a reliable remote exploit capable of spawning a worm through an unpatched security hole in Microsoft’s dominant Windows operating system.

A team of exploit writers led by Kostya Kortchinsky attacked the known SMB v2 vulnerability and created a remote exploit that’s been fitted into Immunity’s Canvas pen-testing platform. The exploit hits all versions of Windows Vista and Windows Server 2008 SP2, according to Immunity’s Dave Aitel.


Over on the Washington Post’s SecurityFix blog, Brian Krebs has been doing a phenomenal job highlighting the online bank robberies — using malware — against small businesses in the United States.
The latest installment, which looks at the role of “money mules” in the cybercrime operation is required reading.

The Web is a dirty, hostile place not fit for use by most decent people, a place where even many seemingly legitimate sites are infested with malware, password-stealing Trojans and all manner of other nasty applications. And it’s getting worse by the minute, according to a new threat report from Websense.

The last couple of years have seen a dramatic rise in the number and quality of malware-as-a-service and hacking-as-a-service providers, with many of them advertising their services on the Web. And while law enforcement officials are well aware of the problem, they’re not having much luck in finding or prosecuting the criminals behind the schemes.

A software engineer who created Trojans for the Swiss authorities to intercept Voice-over-IP (VoIP) phone calls has published the source code to his programs in order to draw attention to the surveillance threat posed by such software. Read the full story [idg.no]

The main site of the Apache Software Foundation was compromised on Friday through an attack using a compromised SSH key, leading to concerns about the integrity of copies of the hugely popular Apache Web server, which is distributed through the Apache.org site.