Jeff Forristal on the Android Master-Key Vulnerability
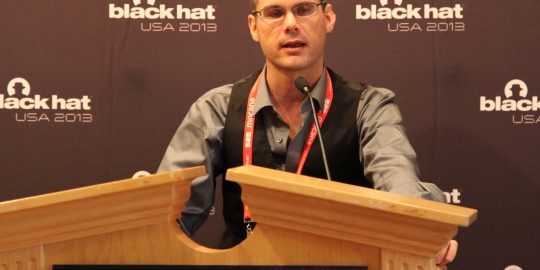
When news of the Android master-key vulnerability began leaking out in early July, details were hard to come by, and that was done intentionally. The researchers at Blue Box Security, a mobile-security start-up, had discovered the vulnerability and were planning to disclose the details of the bug in a presentation at the Black Hat USA 2013 conference.