Vulnerabilities


Tor Urges Users to Leave Windows

In a critical security advisory issued over the weekend, the Tor Project told its users that they should seriously consider migrating out of Microsoft’s Windows operating system.

Mixed Content Blocking Appears in Firefox 23

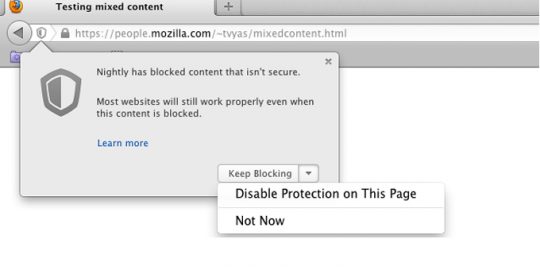
The long-anticipated inclusion of mixed-content blocking in Mozilla Firefox is now at hand, with the security feature showing up in the just-released Firefox 23. The feature, which helps defend users against certain kinds of man-in-the-middle attacks, is on by default in the new browser.


The Black Hat conference is one of the best opportunities each year to see new and innovative research, commune with some of the smartest folks in the industry and generally get a sense of where things stand and where they’re going. This year’s conference was one of the larger in history, both in terms of number of attendees and volume of presentations, and there was a lot to see and hear. With 11 research tracks, keynotes and press conferences happening from morning till night, it was impossible to see it all, even for the most motivated and caffeinated person.

When news of the Android master-key vulnerability began leaking out in early July, details were hard to come by, and that was done intentionally. The researchers at Blue Box Security, a mobile-security start-up, had discovered the vulnerability and were planning to disclose the details of the bug in a presentation at the Black Hat USA 2013 conference.

The vulnerability in Firefox that was being used to exploit some users of Tor in recent days was fixed in a previous Firefox release and the exploit in circulation only works against people running Firefox 17. Over the weekend, word spread that the exploit was in the wild and that the Tor network itself had been compromised, however Tor officials said that was not the case and it was one specific hosting provider who hosts some Tor Hidden Services servers that had been targeted.

Security researchers have been warning about the weaknesses and issues with JavaScript and iframes for years now, but the problem goes far deeper than even many of them thought. A researcher in the U.K. has developed a new technique that uses a combination of JavaScript-based timing attacks and other tactics to read any information he wants from a targeted user’s browser and sites the victim is logged into. The attack works on all of the major browsers and researchers say there’s no simple fix to prevent it.

Las Vegas – In the last Black Hat briefing of the day Wednesday, German security researcher Karsten Nohl of Security Research Labs demonstrated a SIM card attack that exploited sloppy encryption and gave the researcher root access to a type of SIM card built into billions of mobile devices.

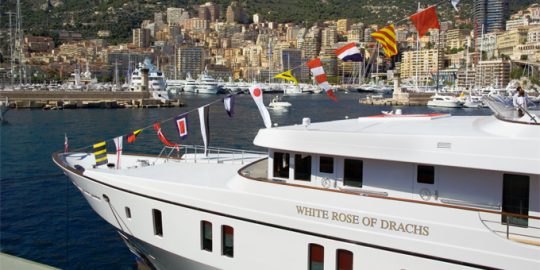
A 213-foot luxury yacht veered off course while cruising in the Mediterranean Sea this summer after a radio navigation research team led by global positioning systems expert Todd Humphreys of the University of Texas Austin built a custom-made device capable of overriding the ship’s GPS receivers with spoofed signals.