Vulnerabilities


Windows 8 Malware Using Google Docs to Target Brazilians

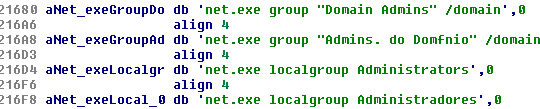
New malware targeting Windows 8 appears to be using Google Docs as a proxy server instead of directly connecting to a command and control (C&C) server. According to research done by Symantec and discussed in the company’s Security Response blog late last week, a Trojan, Backdoor.Makadocs, targets Windows 8 – along with Windows Server 2012 – yet doesn’t use any of the software’s particular functions as an exploit vector.
Adequate Attack Data and Threat Information Sharing No Longer a Luxury

BOSTON – While some industry groups such as the Financial Services Information Sharing and Analysis Center (FS-ISAC) and cross-industry groups such as the Advanced Cyber Security Center (ACSC) facilitate the exchange of threat information, for the most part organizations are still hamstrung by legal constraints and other business factors that prevent an adequate flow of actionable information.


Google has divulged more information about its forthcoming application verifier for the Android operating system. The feature is being rolled out over the air alongside the latest build of the OS, Jelly Bean 4.2, on Nexus 7 and Galaxy Nexus devices as of yesterday.While it can be disabled, the app verifier feature is turned on by default according to a new description from Google/Nexus that describes the process as follows:

Microsoft released its monthly security updates today and put special urgency on a cumulative security update for Internet Explorer 9. Critical vulnerabilities were found in the way the browser handles objects in memory which could lead to an attacker remotely executing code. Victims would have to land on a website hosting an exploit, Microsoft said. The company said there are no public exploits for this vulnerability.

Google has released Chrome 23, the latest version of its browser, which includes fixes for 12 vulnerabilities in the Windows version and two other flaws that are specific only to Mac OS X. The company also handed out $9,000 in rewards to security researchers who reported the vulnerabilities.