Web Security


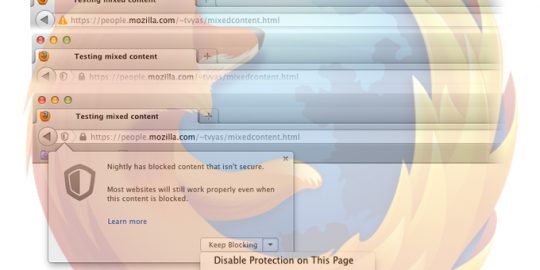
Firefox Adds Mixed Content Blocking by Default

The proliferation of SSL-protected sites has been a boon for security conscious Web users in the last couple of years, as more and more sites have taken the step of offering encrypted connections for sensitive sessions. But one of the problems that’s cropped up is that the dynamic nature of today’s Web means that content […]

OpenSSL Man-in-the-Middle Flaw Fixed in Ruby

The maintainers of Ruby have fixed a serious flaw in its SSL client that could have allowed an attacker to conduct man-in-the-middle attacks by spoofing an SSL server. The vulnerability lies in the OpenSSL toolkit that’s built in to Ruby and is present in several versions of the software from 1.8 through 2.0. An attacker exploiting the […]

mozilla security update

14 Vulnerabilities Fixed in Firefox 22

Mozilla has fixed 14 security vulnerabilities in Firefox, including four critical flaws that could allow remote code execution. There also are six high-severity vulnerabilities fixed in Firefox 22.


The source code for the Carberp Trojan, which typically sells for $40,000 on the underground, has been leaked and is now available to anyone who wants it. The leak has echoes of the release of the Zeus crimeware source code a couple of years ago and has security researchers concerned that it may lead to a similar crop of new Trojans and crimeware kits.

A site outage and redirection on LinkedIn’s site Wednesday night blamed on a DNS problem has security experts and users worried that the networking site’s DNS records may have been compromised, along with those of several other sites. But it appears the issue may have been caused by a simple mistake.

There is a massive stack of Java patches on deck for tomorrow, with Oracle planning to fix 40 vulnerabilities in a number of different components of Java SE. Nearly all of the vulnerabilities are remotely exploitable. Oracle doesn’t release much in the way of information about the content of its patch updates before the fixes […]