
Microsoft Provides Guidance on Mitigating DDE Attacks
Microsoft published guidance for Windows admins on how to safely disable Dynamic Data Exchange (DDE) fields in Office that are being used to spread malware in email-based attacks.
Microsoft published guidance for Windows admins on how to safely disable Dynamic Data Exchange (DDE) fields in Office that are being used to spread malware in email-based attacks.
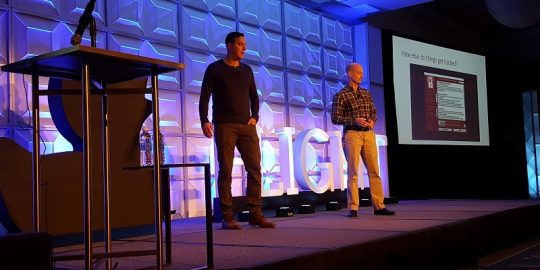
Security experts Charlie Miller and Chris Valasek, contemplate the larger universe of the Internet of things and security.

Questions brew over whether Mantistek GK2 Mechanical Gaming Keyboard is snooping on users as they type.

Enterprises are grappling with widespread incidents of misconfigured servers leaking sensitive data to the public internet.

The Tor Project released a patch for a vulnerability that leaks the real IP addresses of macOS and Linux users of its Tor Browser.

Zeus Panda, a banking Trojan designed to steal credentials, is being distributed via poisoned Google search results.

Researcher Troy Hunt discovers as far as the internet has come in adopting HTTPS, it still has a ways to go.

A bug exploitable in WordPress 4.8.2 and earlier creates unexpected and unsafe conditions ripe for a SQL-injection attack.

A cybercrime outfit stealing from as many as 10 banks in Russia, Armenia and Malaysia has borrowed heavily from one of the kingpins in this realm, Carbanak.

Firefox is to stop using the privacy-busting canvas-based browser fingerprinting that allows websites to track users’ online activities.
Infosec Insider content is written by a trusted community of Threatpost cybersecurity subject matter experts. Each contribution has a goal of bringing a unique voice to important cybersecurity topics. Content strives to be of the highest quality, objective and non-commercial.
Sponsored Content is paid for by an advertiser. Sponsored content is written and edited by members of our sponsor community. This content creates an opportunity for a sponsor to provide insight and commentary from their point-of-view directly to the Threatpost audience. The Threatpost editorial team does not participate in the writing or editing of Sponsored Content.


