Web Security


New ransomware locks PCs, demands premium SMS for removal

From ZDNet (Dancho Danchev)
PandaLabs is reporting on a newly discovered ransomware variant [pandasecurity.com]which locks the affected user’s PC, and demands a premium SMS in order to deactivate it.
The ransomware doesn’t have any self-propagation functions and appears to be coming under the form of a typical fake codec that has been affecting users for over a week now. The message (in Russian) demands that the affected user sends an SMS with the pseudo-unique number to the given number in order to receive deactivation code. Read the full story [zdnet.com]

85% of malicious sites only online for 24 hours

From PC Advisor (Carrie-Ann Skinner)

More than 80 percent of websites that had been poisoned with malicious code between 2008 and 2009 were removed within 24 hours, says AVG.

The security vendor’s Web Threat Profile Report estimated that on any one day between 8 and 14 million web users are being exposed to social engineering scams, such hoax Facebook pages or rogue security apps that encourages surfers to download malicious software to their PC. Read the full story [cio.com]

5 security flubs users make while Web surfing

From CIO (Joan Goodchild)
You can install the best firewalls, patch religiously, and make sure your anti-virus software is always up-to-date, but there is one online risk factor you can never control: the user. Whether they are downloading dangerous content or falling prey to phishing scams, the end user continues to be the toughest security risk to mitigate in most organizations.
With that constant struggle in mind, giving users education about what they are doing and why it is dangerous is the more effective strategy. Here are some of the more common security missteps users take and some advice [cio.com] on how to stay secure online.


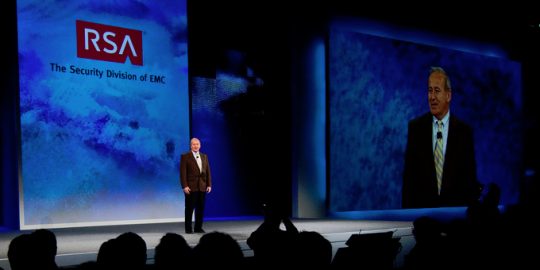
Scott Charney used his keynote speech at the RSA Conference on Tuesday to talk up a variety of hardware and software-based technologies meant to infuse the Internet with more trust. Charney, the head of Microsoft’s Trustworthy Computing team, talked about the need for greater adoption of TPMs, code signing and identity systems, all of which […]

Google has a reputation for being open and transparent with many of its initiatives and internal workings, but one of the things that the company hasn’t talked much about publicly until recently is security. In this interview with SearchSecurity.com, the director of security for Google Apps, Eran Feigenbaum, discusses the company’s plans for security around cloud computing and how the model affects compliance efforts.

From Microsoft’s SDL blog (Chris Weber)
I’m writing to tell you about our new Watcher tool for web-app security auditing and testing.  Watcher is a plug-in for Eric Lawrence’s Fiddler proxy aimed at helping developers and testers find security issues in their web-apps fast and effortlessly.  Because it works passively at runtime, you have to drive it by opening a browser and cruising through your web-app as an end user.  For the developer, the tool can provide a quick sanity check, so you can find problems and hot-spots that warrant further attention.  In the hands of a pen-tester it can assist in finding issues that lead to other attacks like XSS and CSRF. Read the full story [msdn.com]

By David Mortman
I am very excited to be guest blogging about RSA here on Threatpost. A special thank you to Dennis and Ryan for the privilege.

I am also  very excited to once again be speaking at RSA this year. Last year, I was on a panel with Mike Rothman, Rich Mogull, Martin McKeay and Ron Woerner titled “Avoiding Another Security Groundhog Day”. The main theme of our panel was how could we as security practitioners move forward with protecting our customers while avoiding the sins of the past.

From DarkReading (Kelly Jackson Higgins)
Kernel rootkits are tough enough to detect, but now a researcher has demonstrated an even sneakier method of hacking Linux.
The attack exploits [dtors.org PDF] an oft-forgotten function in Linux versions 2.4 and above in order to quietly insert a rootkit into the operating system kernel as a way to hide malware processes, hijack system calls, and open remote backdoors into the machine, for instance. Read the full story [darkreading.com]

From The Register (John Leyden)
Scareware scammers are trying to game search engines into promoting crudware sites when a surfer searches for information on Ford cars.

The Ford scareware campaign [pandasecurity.com] features around one million links, all targeting the Ford Motor Company, designed to trick search engines into promoting malicious pages towards the top of search results. Malvertised pages are punting a rogue anti-virus product, called MS AntiSpyware 2009. The malicious application attempts the scare users into buying useless software on the basis of fraudulent scan results that report systems are infected, whether they are or not. Read the full story [theregister.co.uk]

By Roel Schouwenberg
Over the weekend, we’ve seen a number of Cross Site Scripting worms for Twitter.
 
Now, with all the recent security problems at Twitter,  these worms [networkworld.com] come as little surprise.  The most virulent worm is not particularly complex in the vulnerability it is exploiting. The original author? A bored 17-year-old who had nothing better to do over the Easter weekend.